
Know What Your AI Can Access.
Prove It. Control It.
See what every AI agent is accessing and enforce what it can touch, all without standing up new infrastructure.
- Prove governance: Every AI connection authorized, logged, and traceable to a single identity.
- Remove roadblocks: Connect new agents and tools in an afternoon, with no firewall changes.
- Cut risk: Zero Trust access control for AI.
- Control cost: Cap and attribute every agent’s spend by identity, before the invoice.
Every Ungoverned AI Agent Is Risk and Cost You Can’t See
The Blocker to AI Isn’t the Tech. It’s Governance.
Legacy tools authorize by IP address, share API keys across every workload, and can’t tell you what any single agent is reaching, calling, or costing.
- Every new agent, model, or tool adds another round of firewall, routing, and NAT changes.
- No per-agent visibility into which model, tool, or data source each workload is calling
- Open inbound ports expose LLMs and MCP servers to misuse & attack
- No way to cap or attribute the cost and token spend of individual agents and teams
The network tax: each new deployment adds firewall, NAT, and DNS changes
AI Meets Zero Trust:Identity-First Enclaves That Govern, Secure, and Control the Cost of Every AI Interaction
Closing the governance gap takes three disciplines, built on top of each other.
Know Who and What Is Talking
Every agent, LLM, and MCP server gets its own cryptographic identity, distinct from the humans and service accounts that launched it. Nothing acts under a shared key.
Nothing Connects Until Policy Says So
Policy authorizes each identity before any routable path exists. If policy doesn’t allow the interaction, no connection is made and nothing is reachable.
Where the Enclave Meets Your Data Stack
The enclave bounds what each agent can reach, so the data any component can touch stays small and known. Classification, DLP, and retention stay the work of your data stack, running over an access layer that is already least-privilege.
Get AI Governance and Simplify Deployments by Replacing Firewall Rules with Identity-based Policy
- Every workload gets its own cryptographic identity, not a shared key
- No changes to network topology or firewalls
- Each workload reaches only what service-level policy explicitly permits
- Outbound-only connections, no inbound ports, no firewall holes
- Control and governance follow workload identity, never an IP address
- LLM & MCP Gateways govern model and tool access and spend
The IT & Security Leader’s Guide to AI Governance
Identity, then Access, then Data — the three disciplines above, built out in full, with NIST and CISA alignment and a step-by-step implementation path.
Five Steps to Governed and Secured AI
The three disciplines above describe the model. Here is what happens each time a workload connects, in order.
-
1
Give each workload a cryptographic identity
At enrollment, each workload receives its own certificate-based identity, the credential every later step checks against.
-
2
Every component dials out — nothing listens
Every component dials out and authenticates mutually, which leaves no inbound port open and no public endpoint exposed.
-
3
Policy authorizes each connection before a path exists
At connection time, policy checks that identity and grants only the specific models, tools, and data it allows, before any route is created.
-
4
Every interaction is logged and metered by identity
Because the same identity authorizes and records each connection, you see which agent reached which model or tool and what it consumed.
-
5
You govern access, spend, and models through one console
Grant or revoke access, cap spend, and steer requests between public and private models by editing policy in one place, effective immediately.
Want the architecture in depth — tunnelers, SDKs, the control plane, and enforcement? Explore the platform →
Two Gateways, One Identity Model
The enclave is the architecture. The LLM Gateway and the MCP Gateway are how agents actually reach models and tools. Each is an identity-first enforcement point rather than a new open door.
LLM Gateway
One OpenAI-compatible endpoint across every provider
- Routes across OpenAI, Anthropic, Azure, AWS Bedrock, Google Vertex AI, and Ollama from a single endpoint
- Semantic routing sends each request to the right model, steering routine queries to cheaper or self-hosted options to control spend
- Reaches every model over the NetFoundry fabric, so agents never receive API keys
- Load balancing across model endpoints, with automatic health checks and failover
MCP Gateway
Identity-based access to every MCP server
- Nothing exposed — MCP servers stay private, with no public IP or port
- One command wraps any local stdio MCP server into a shared endpoint, with no code changes
- Aggregates local and remote servers into one namespaced interface
- Security-by-design filtering removes unauthorized tools from the schema entirely, not only at call time
- Each agent gets an isolated session with dedicated backend connections
Behind both gateways, AI agents never get access to API keys, service accounts, shared secrets, or public endpoints. Together the gateways form a Zero Trust landing zone for agents, and NetFoundry can front third-party gateways the same way.
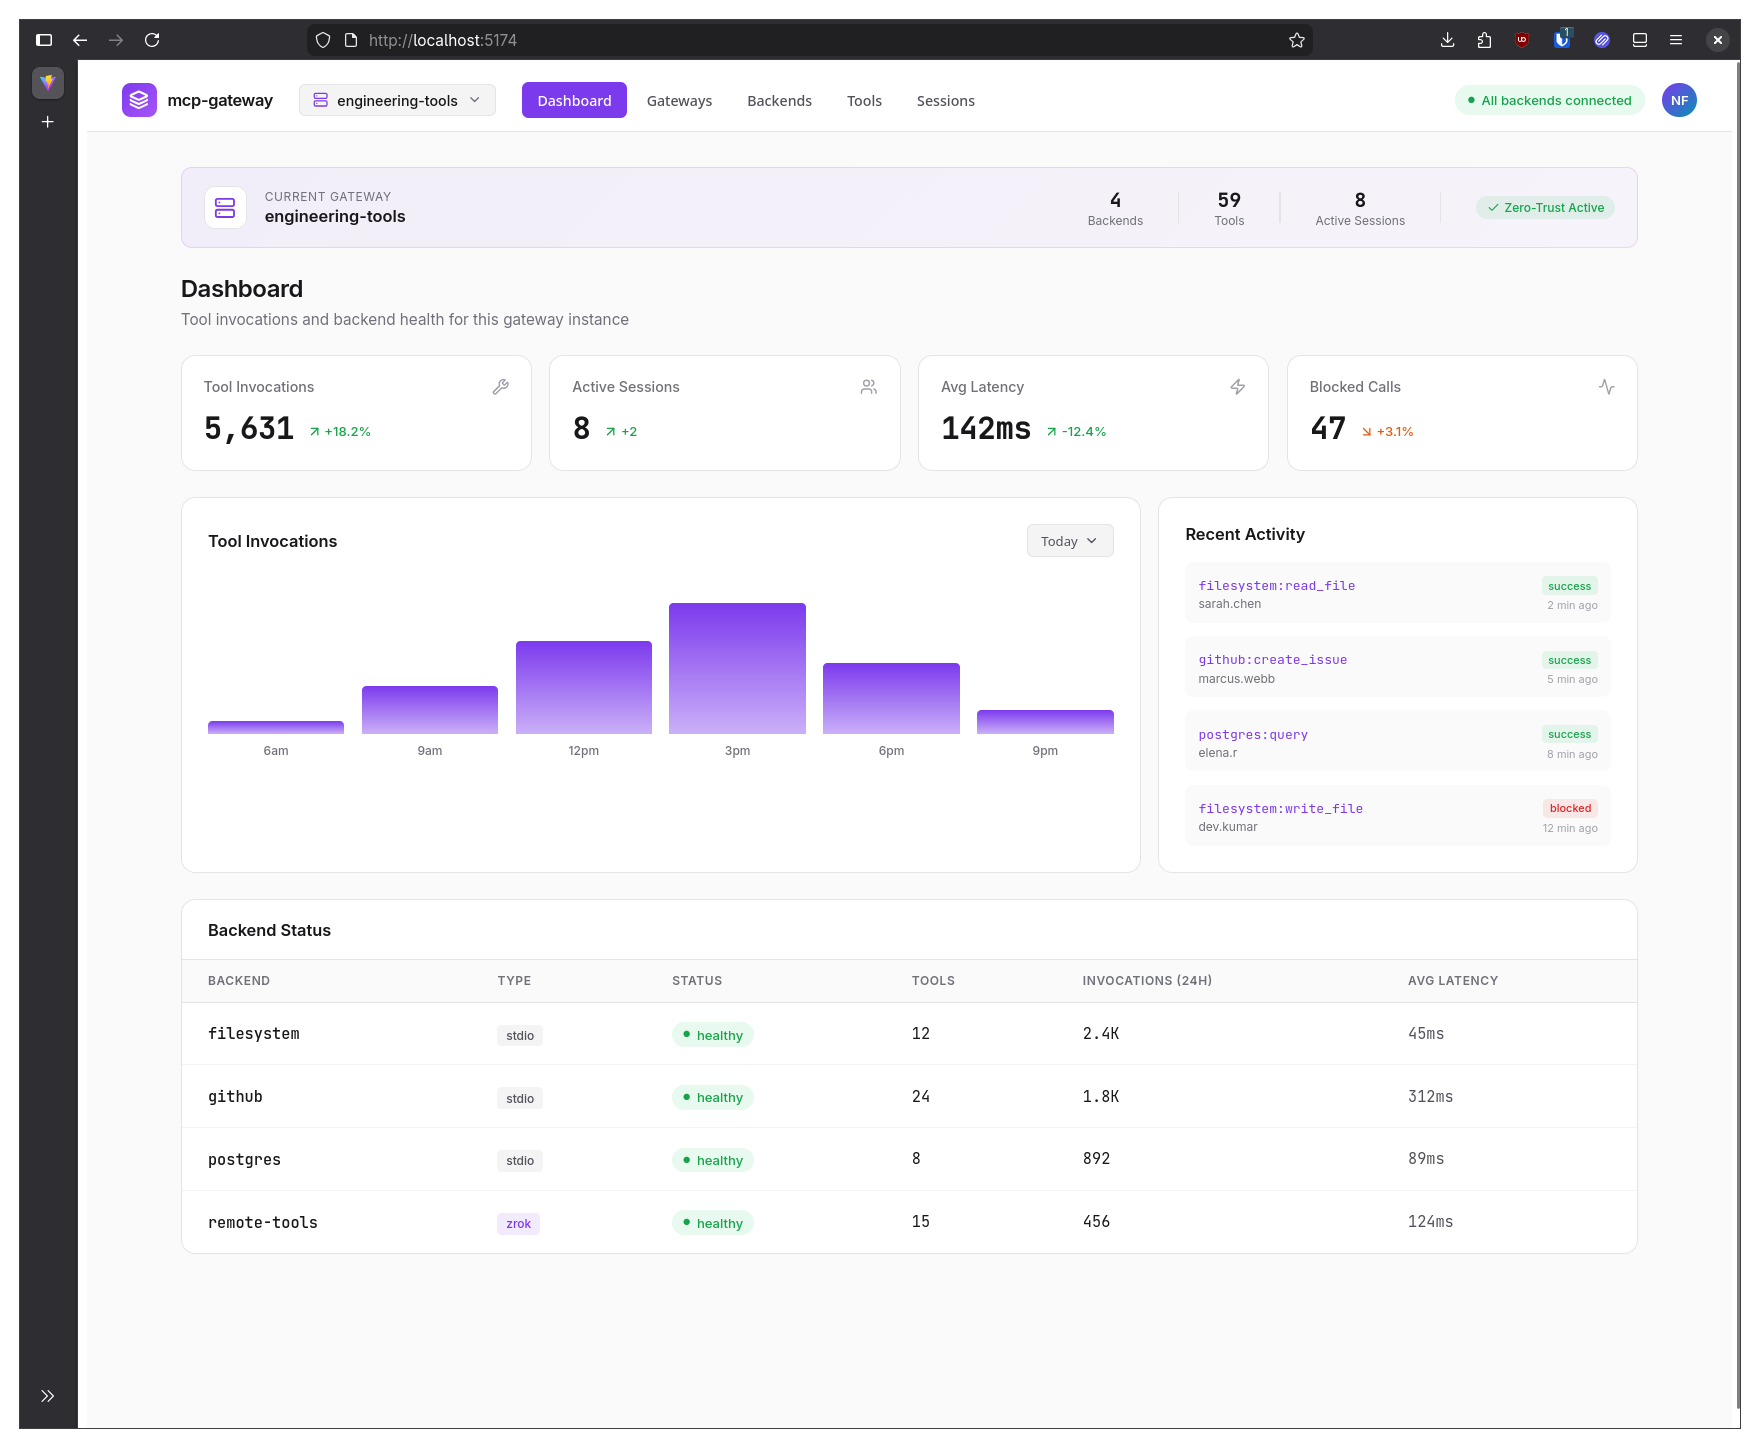
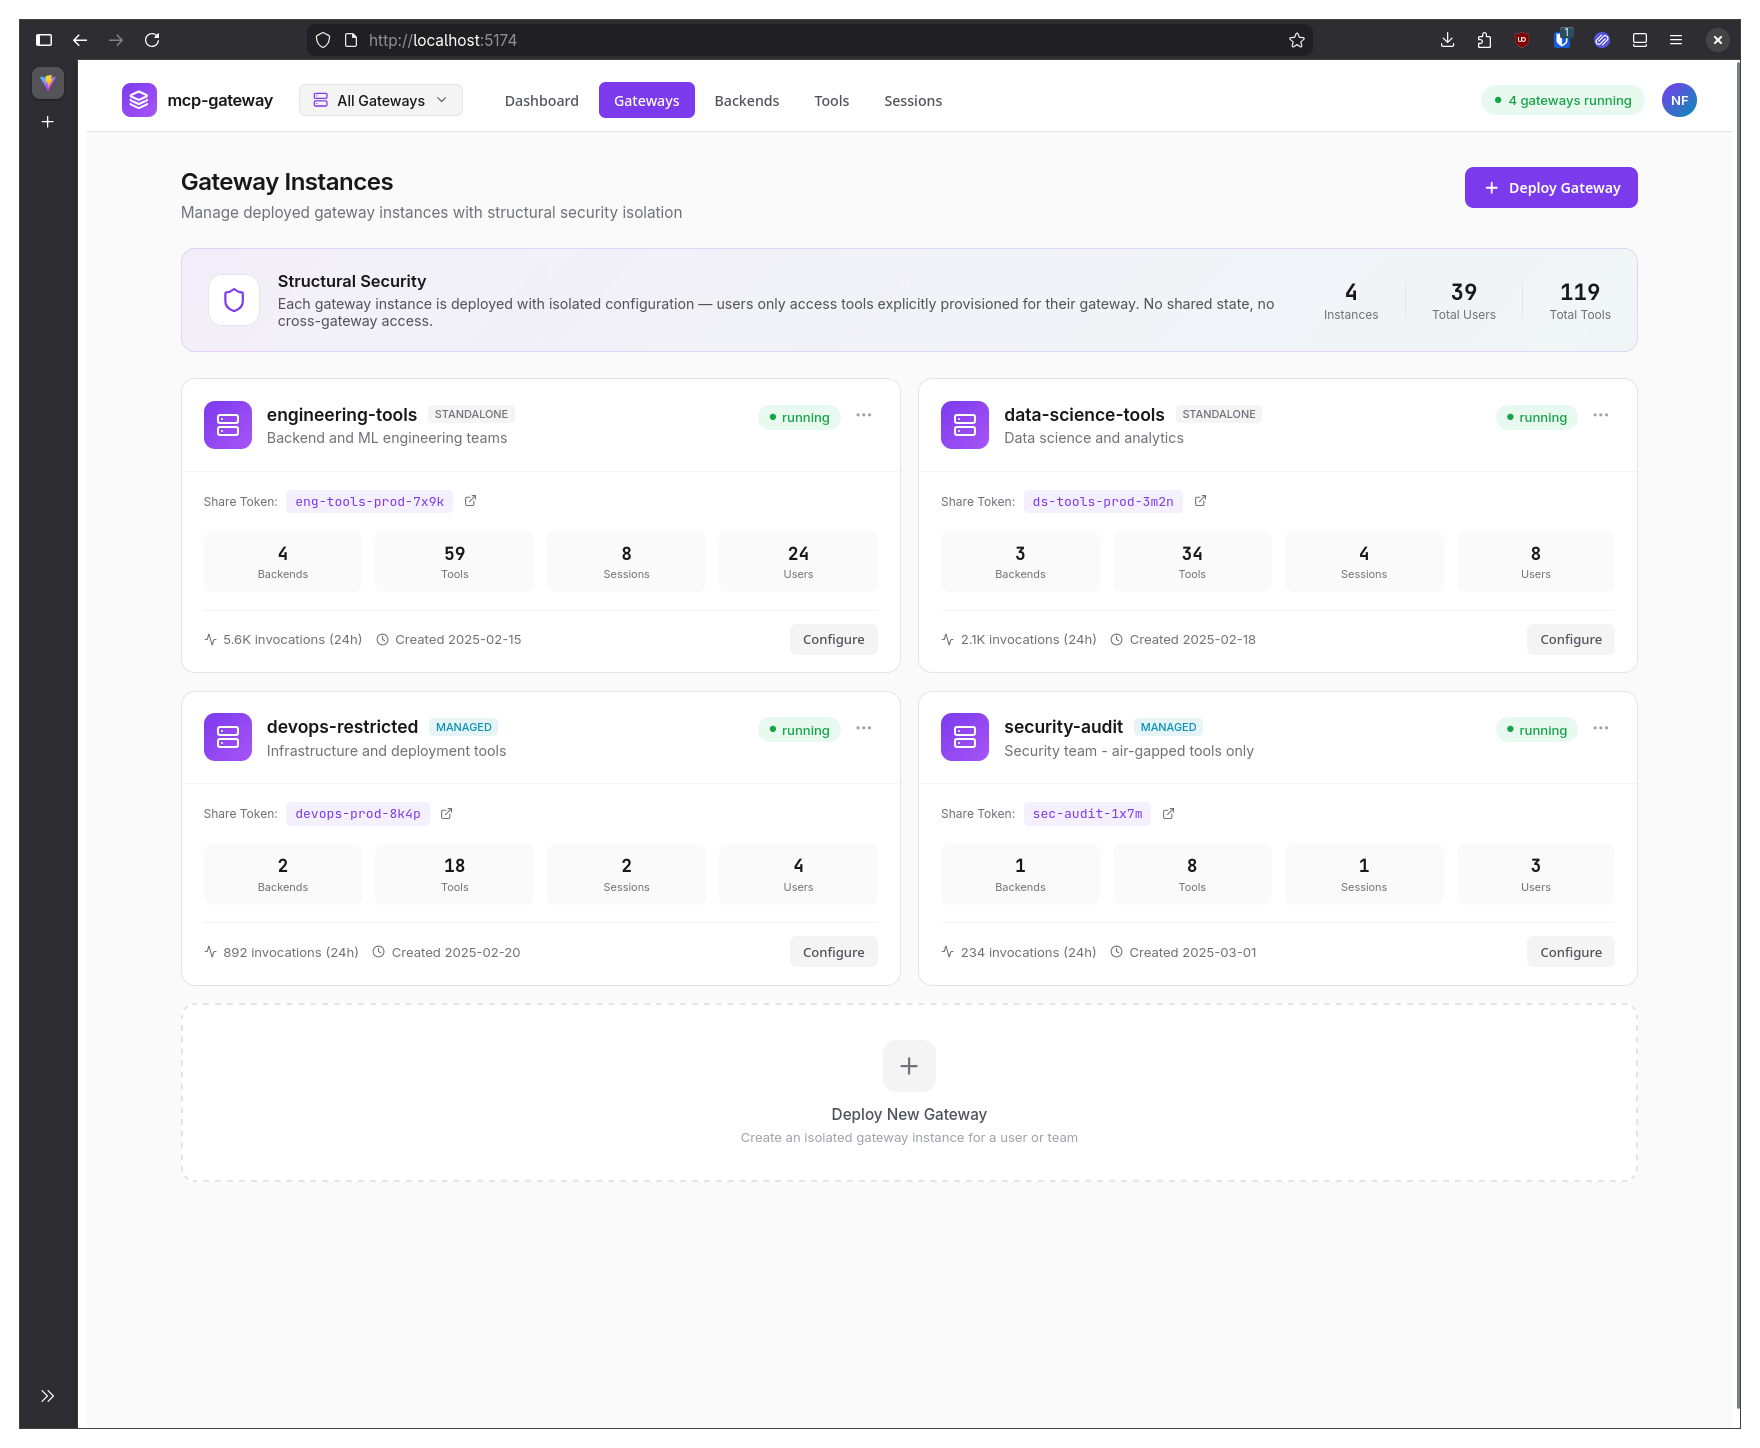
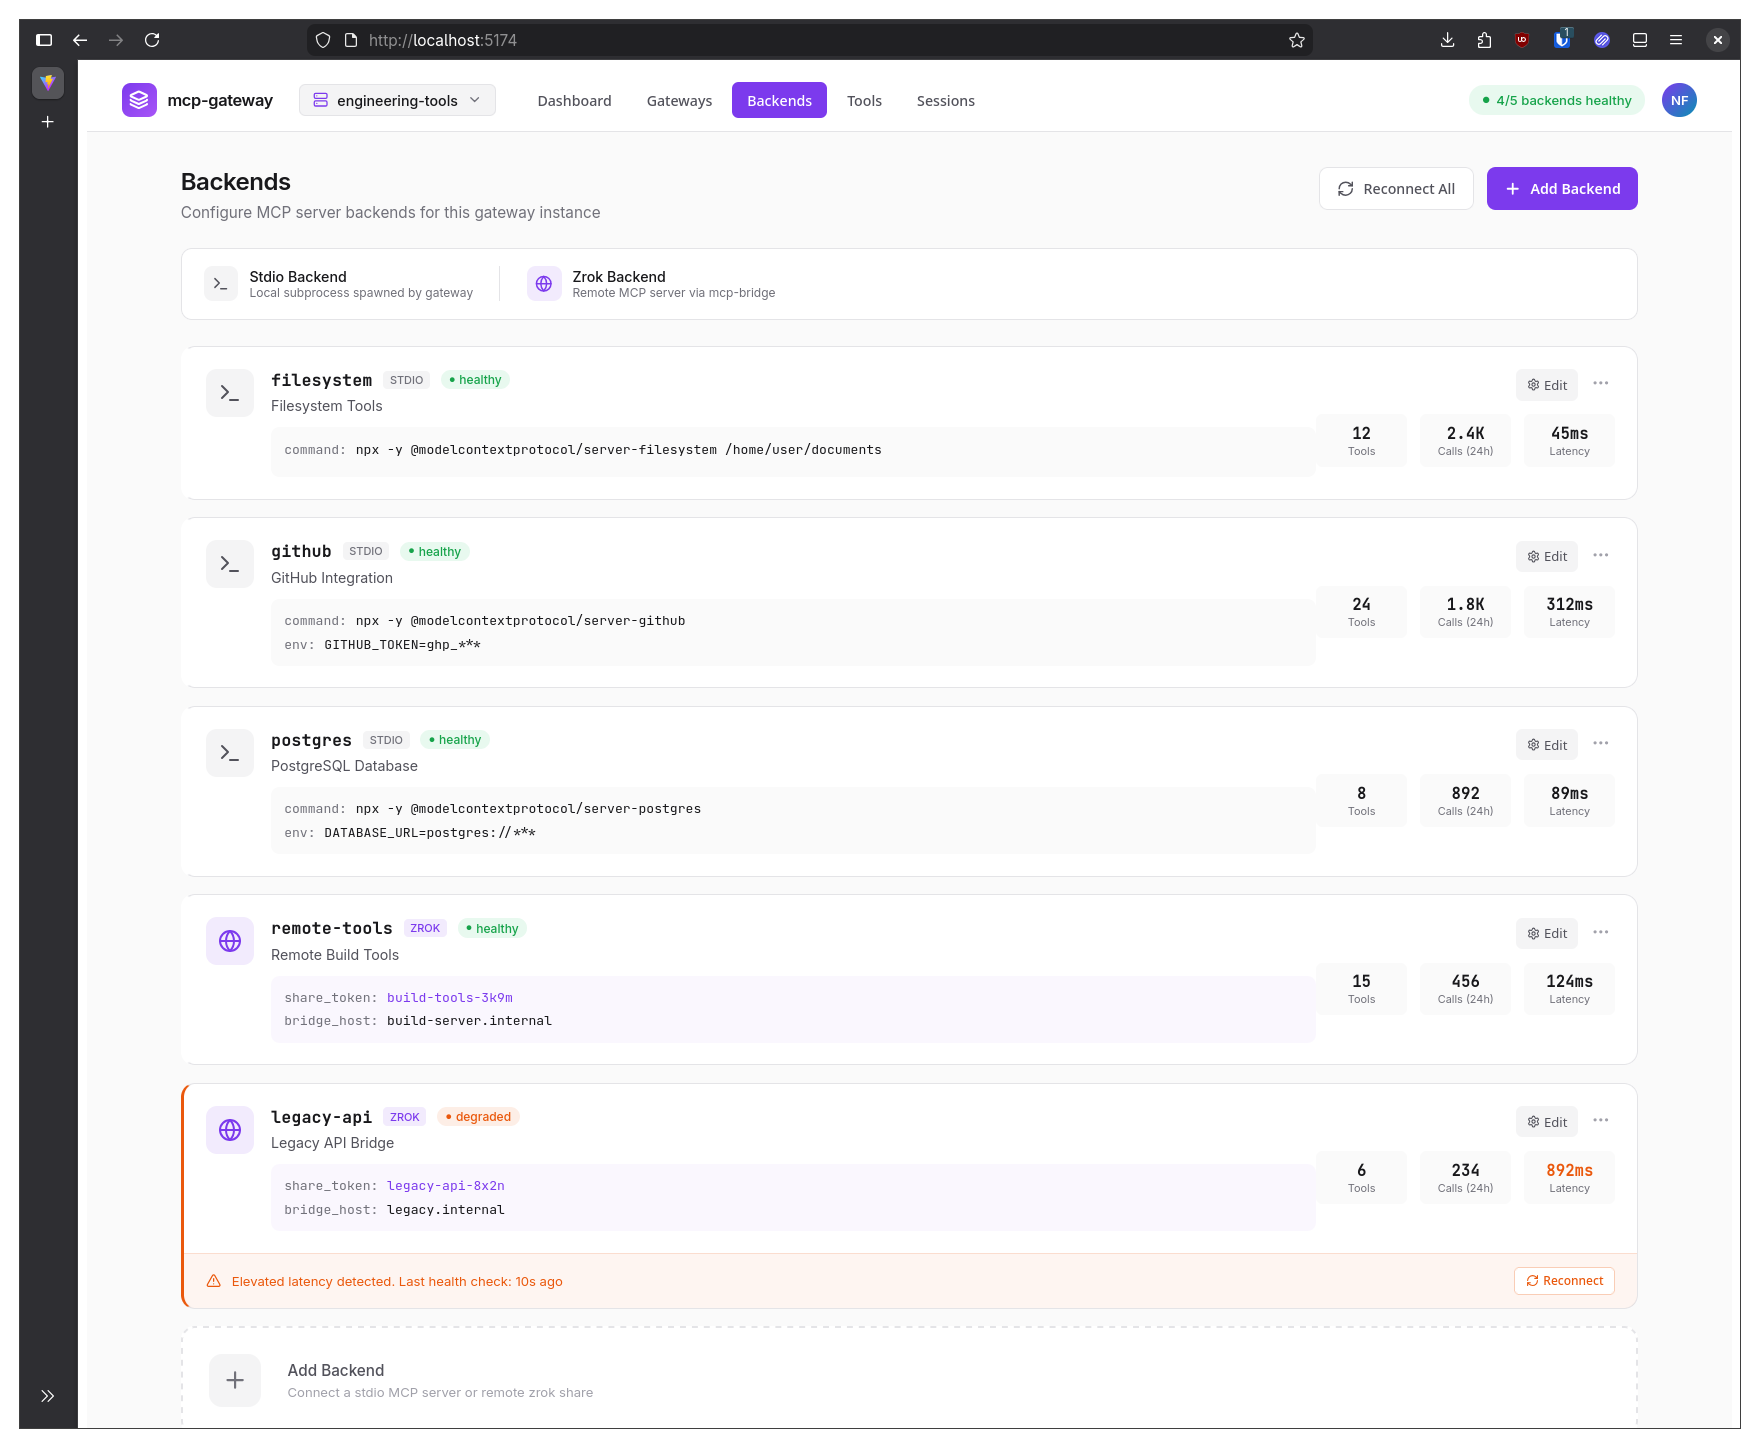
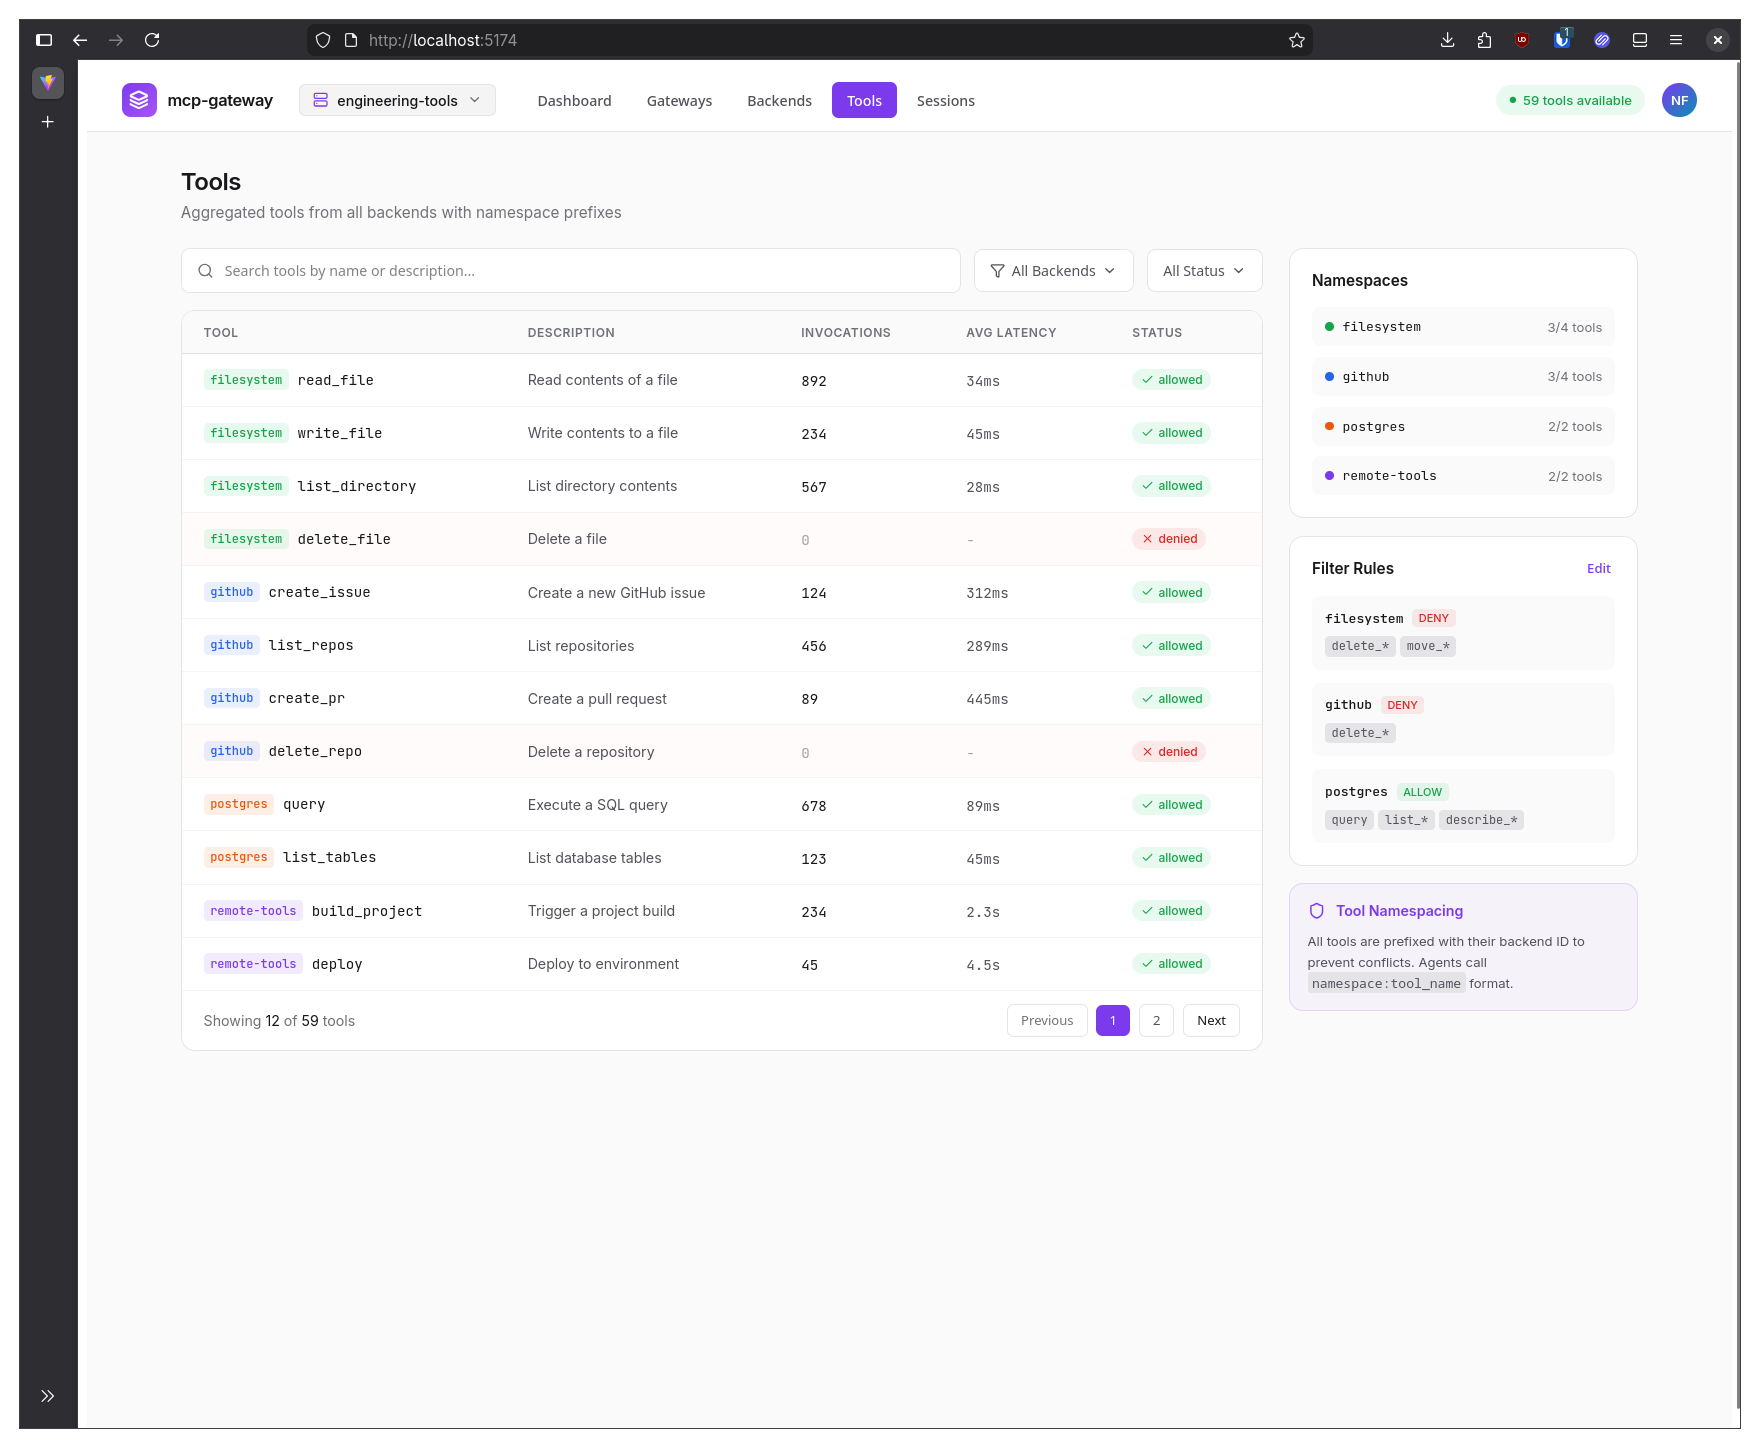
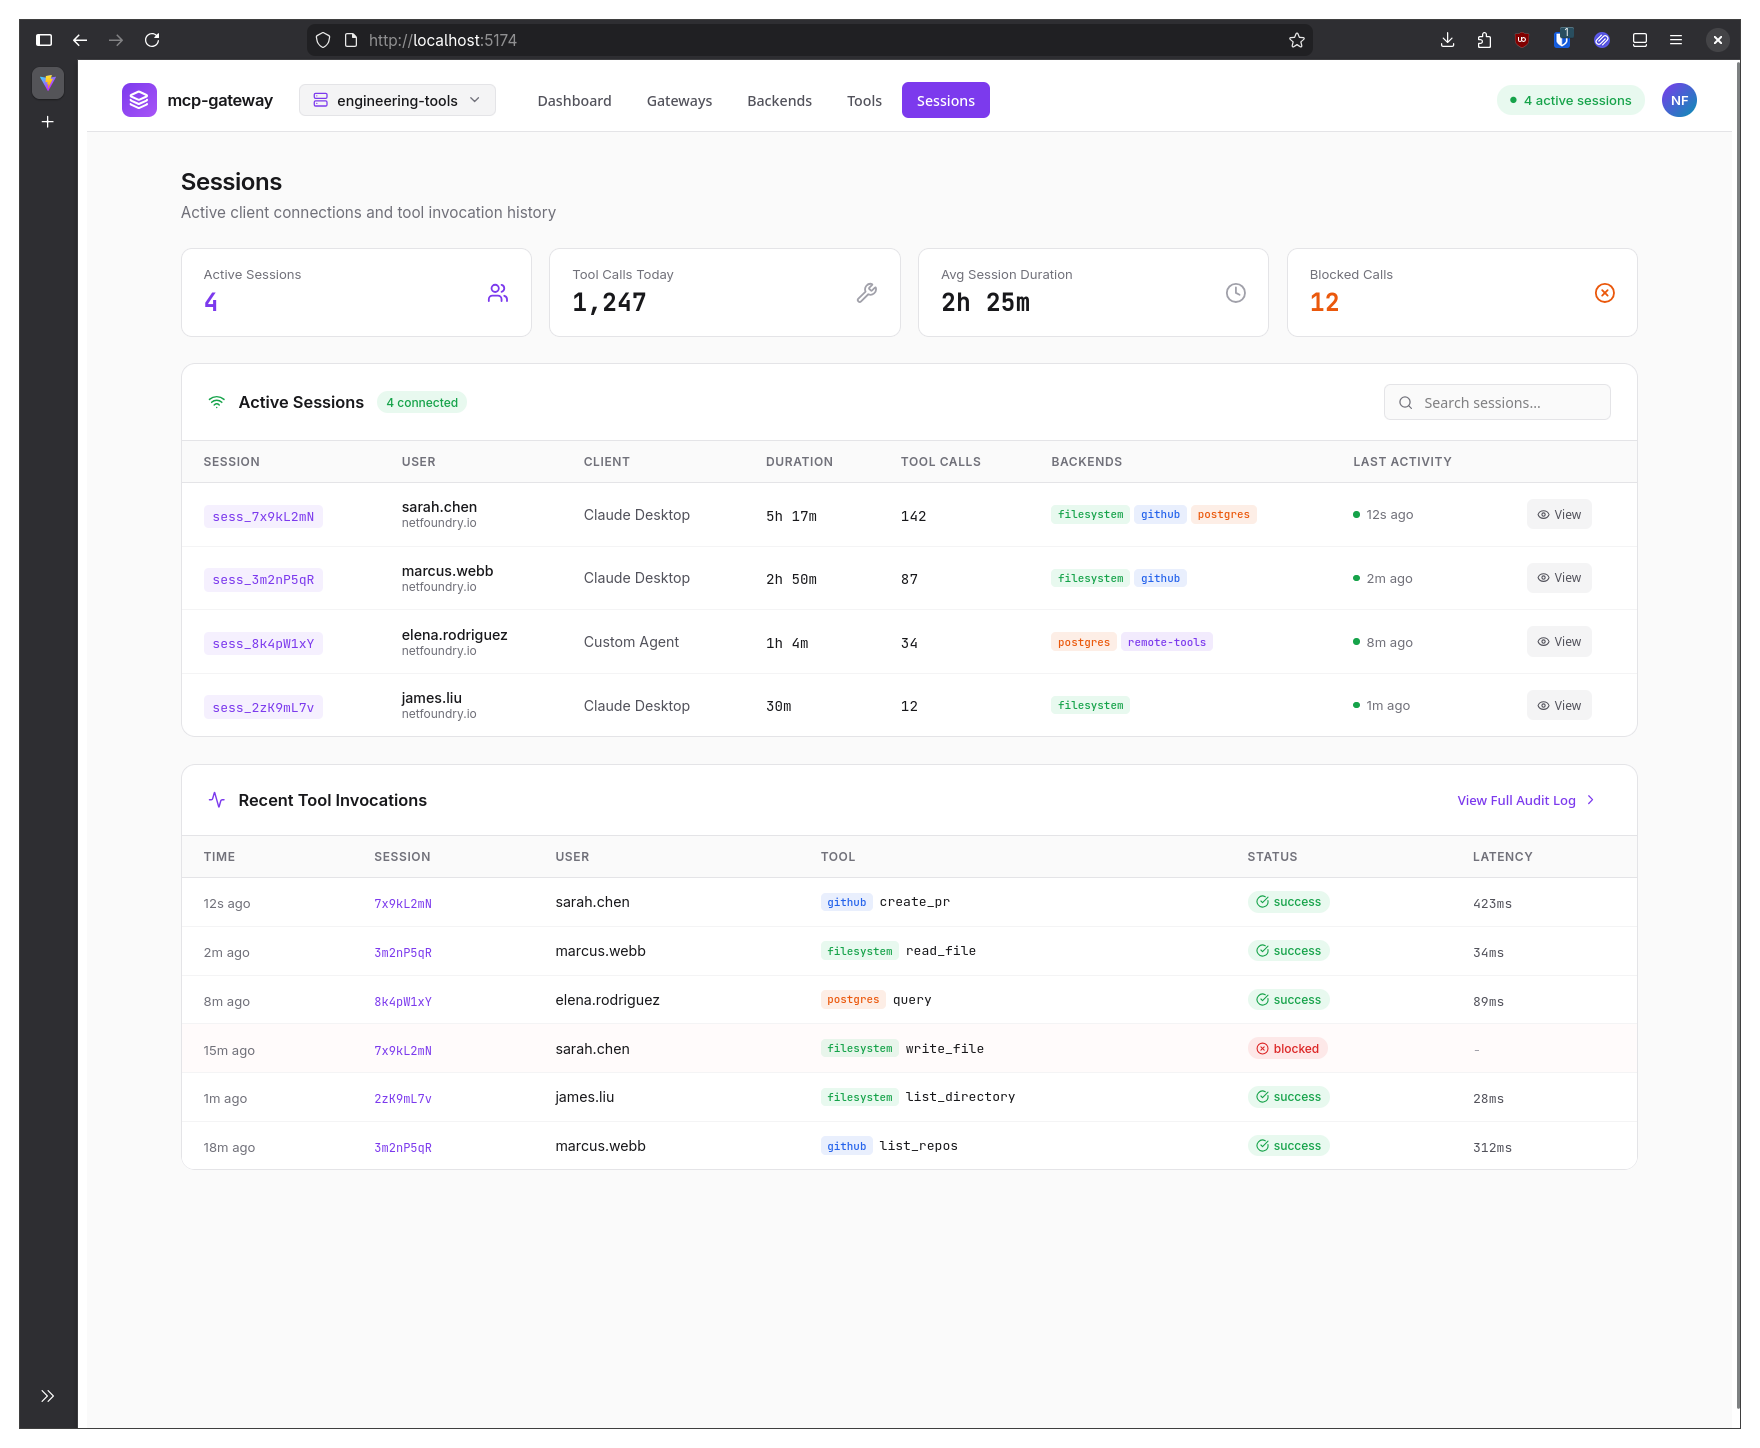
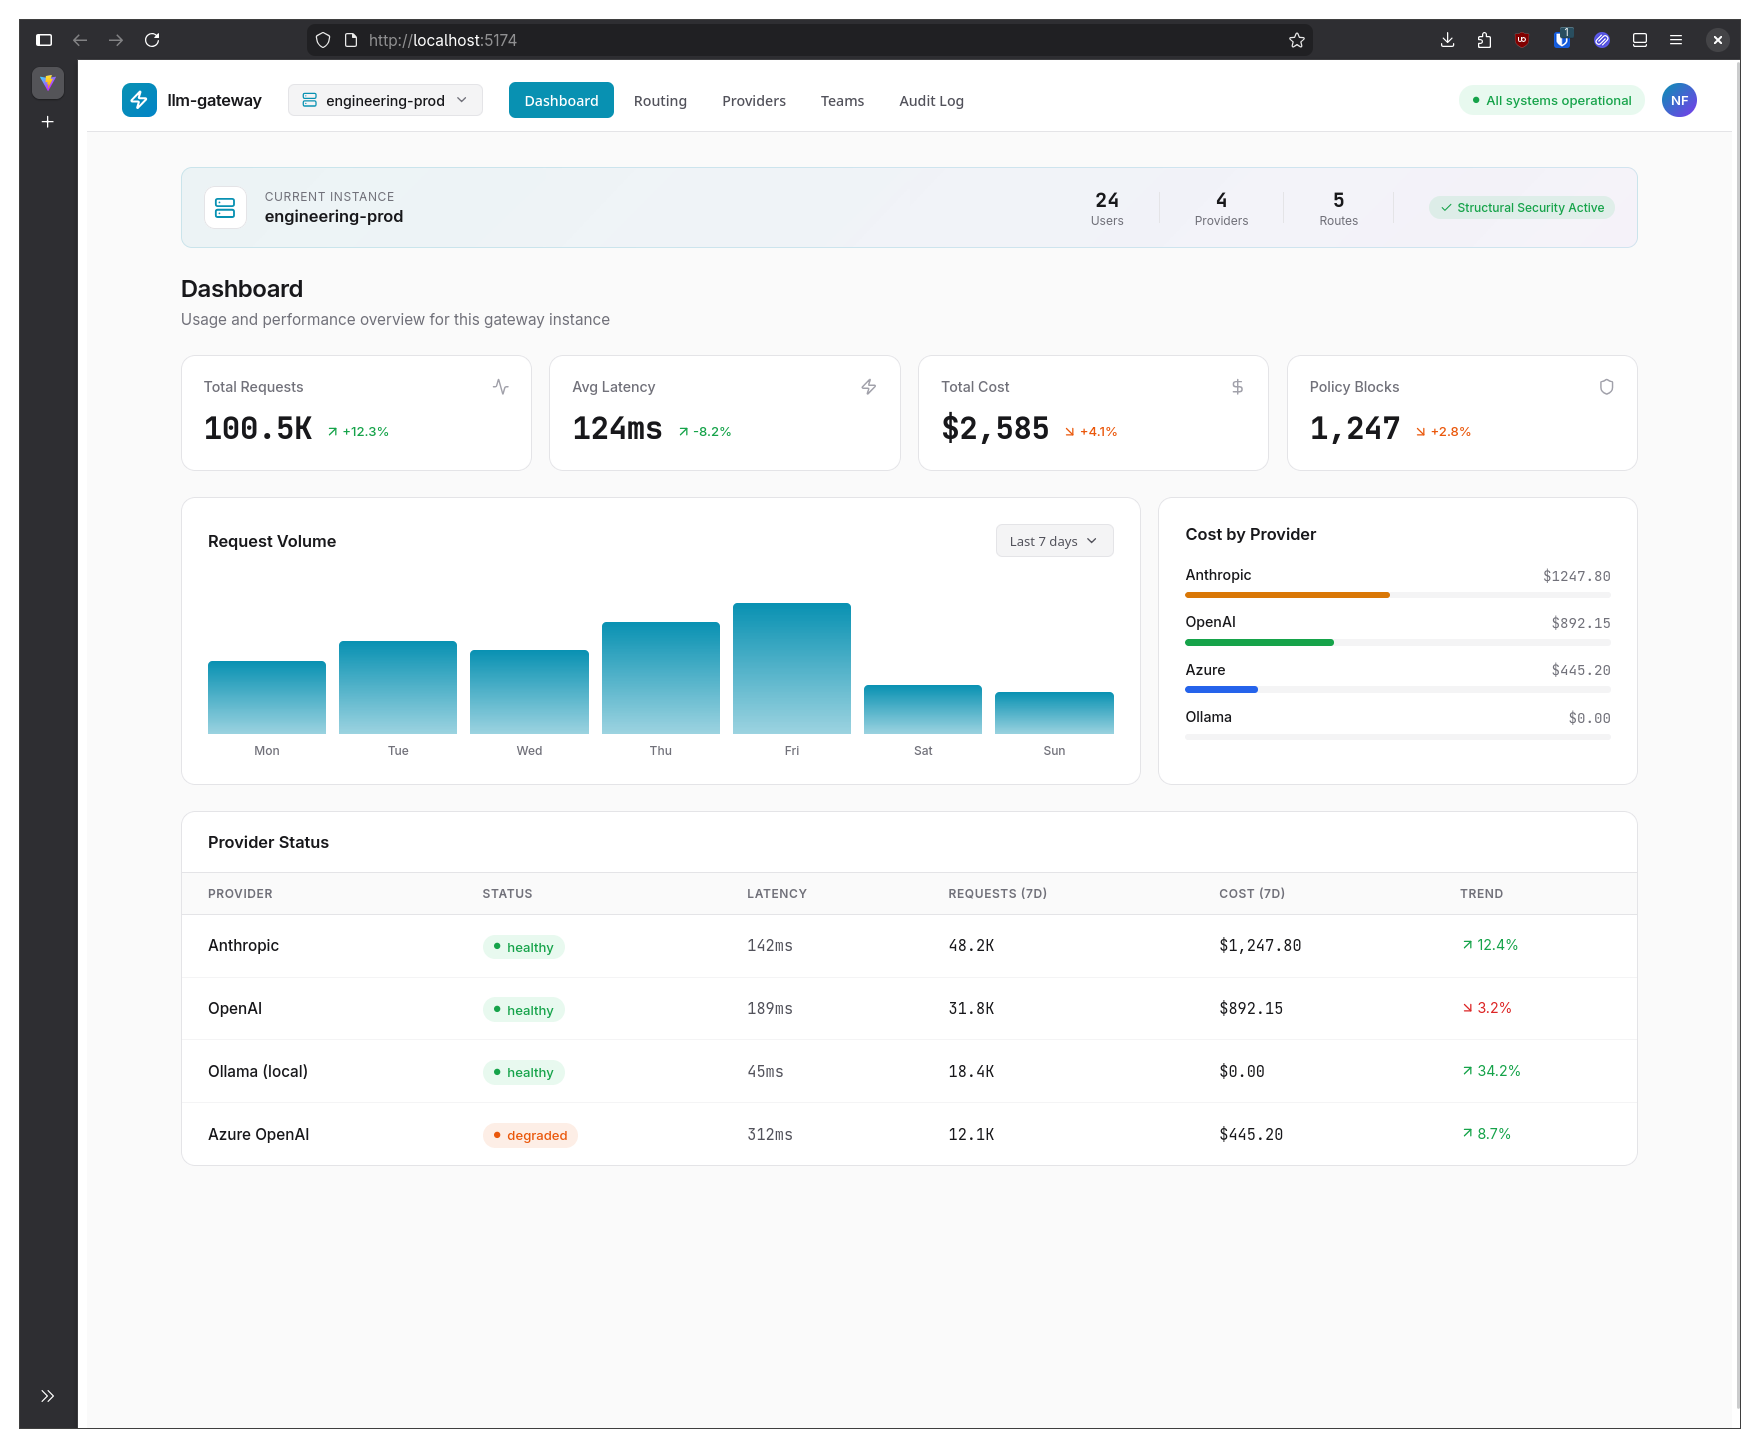
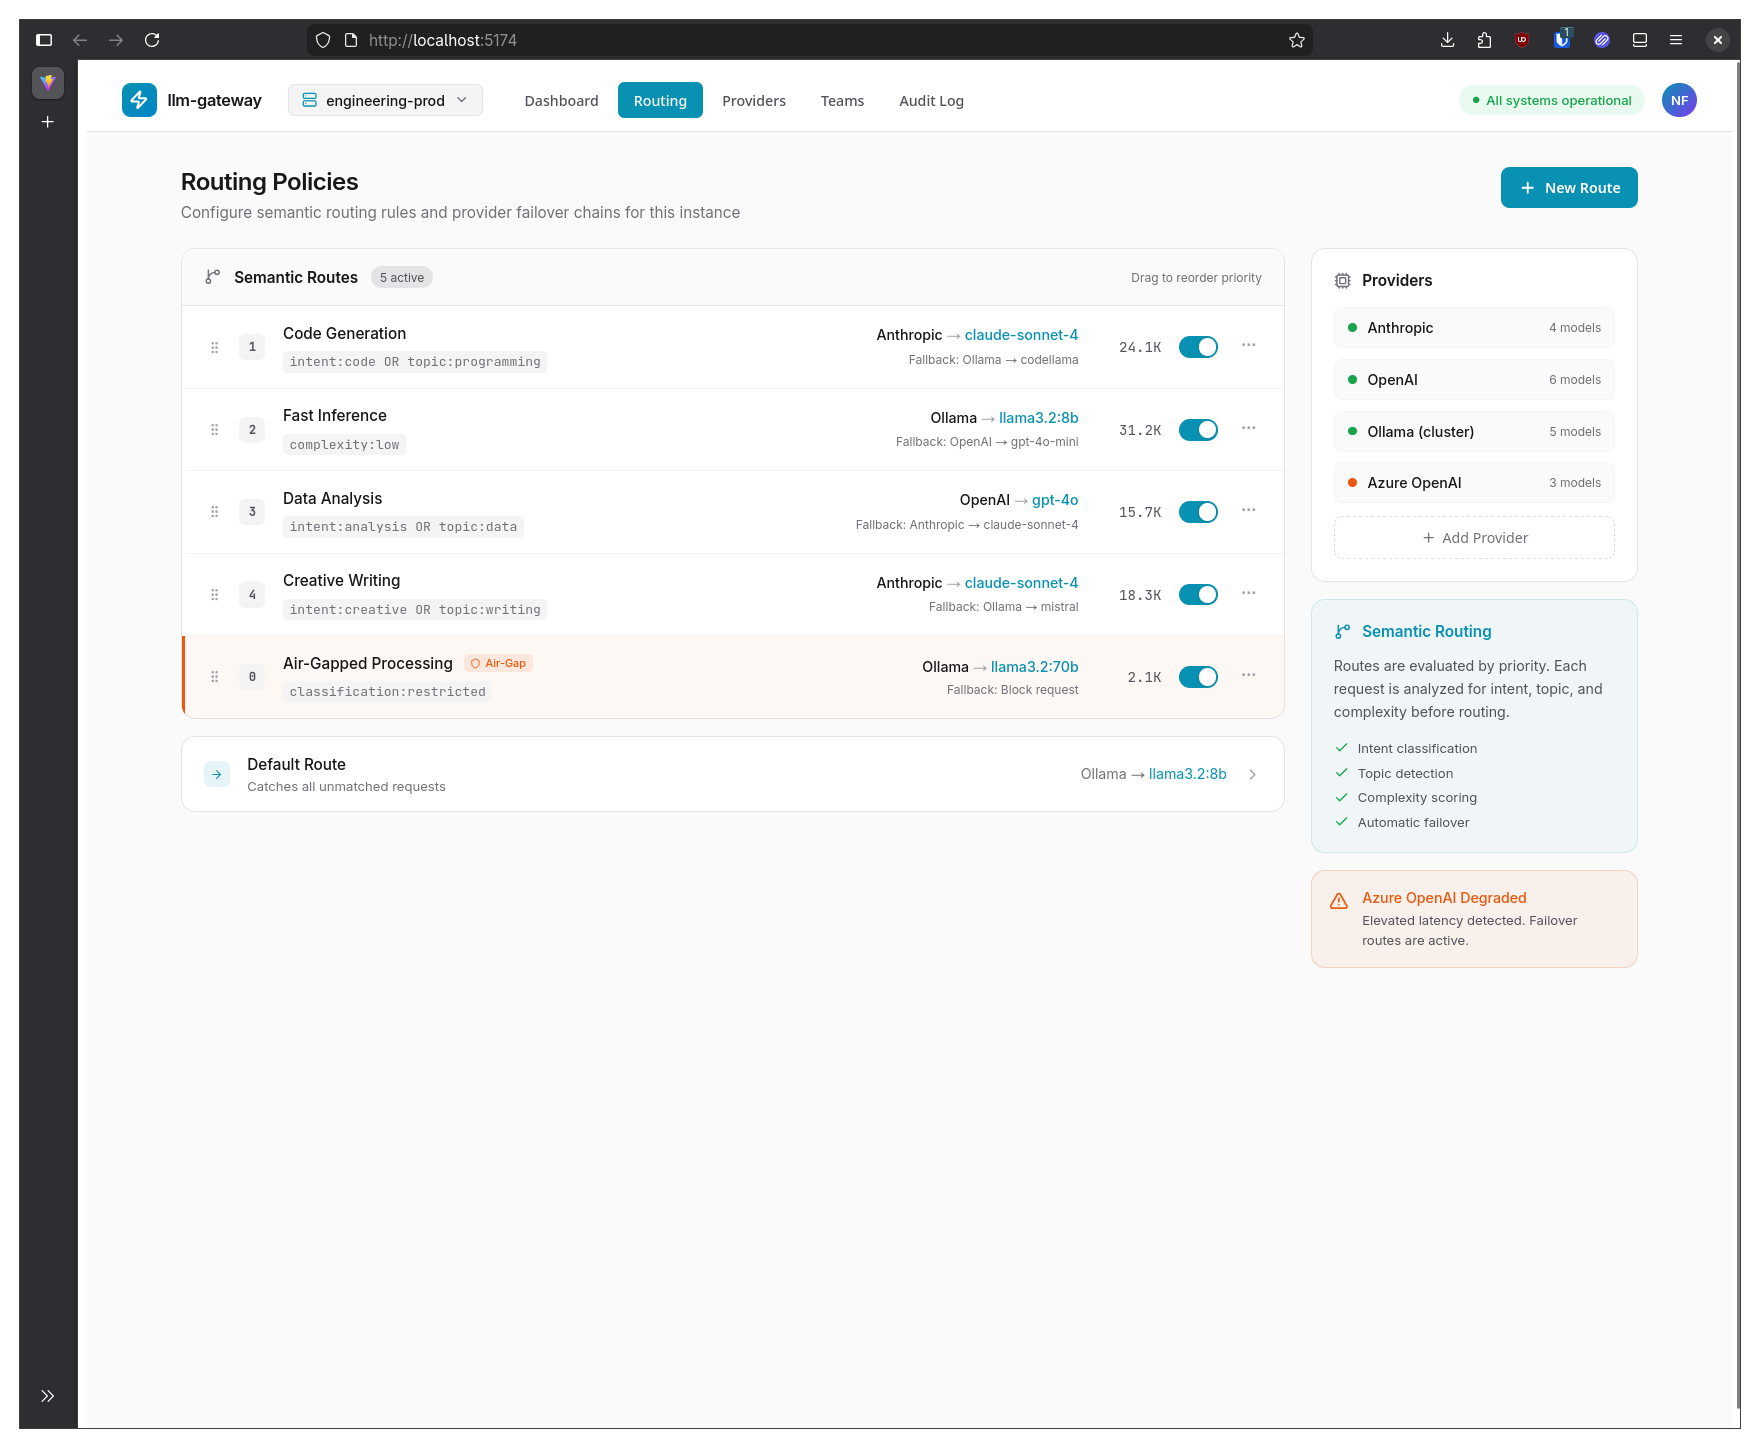
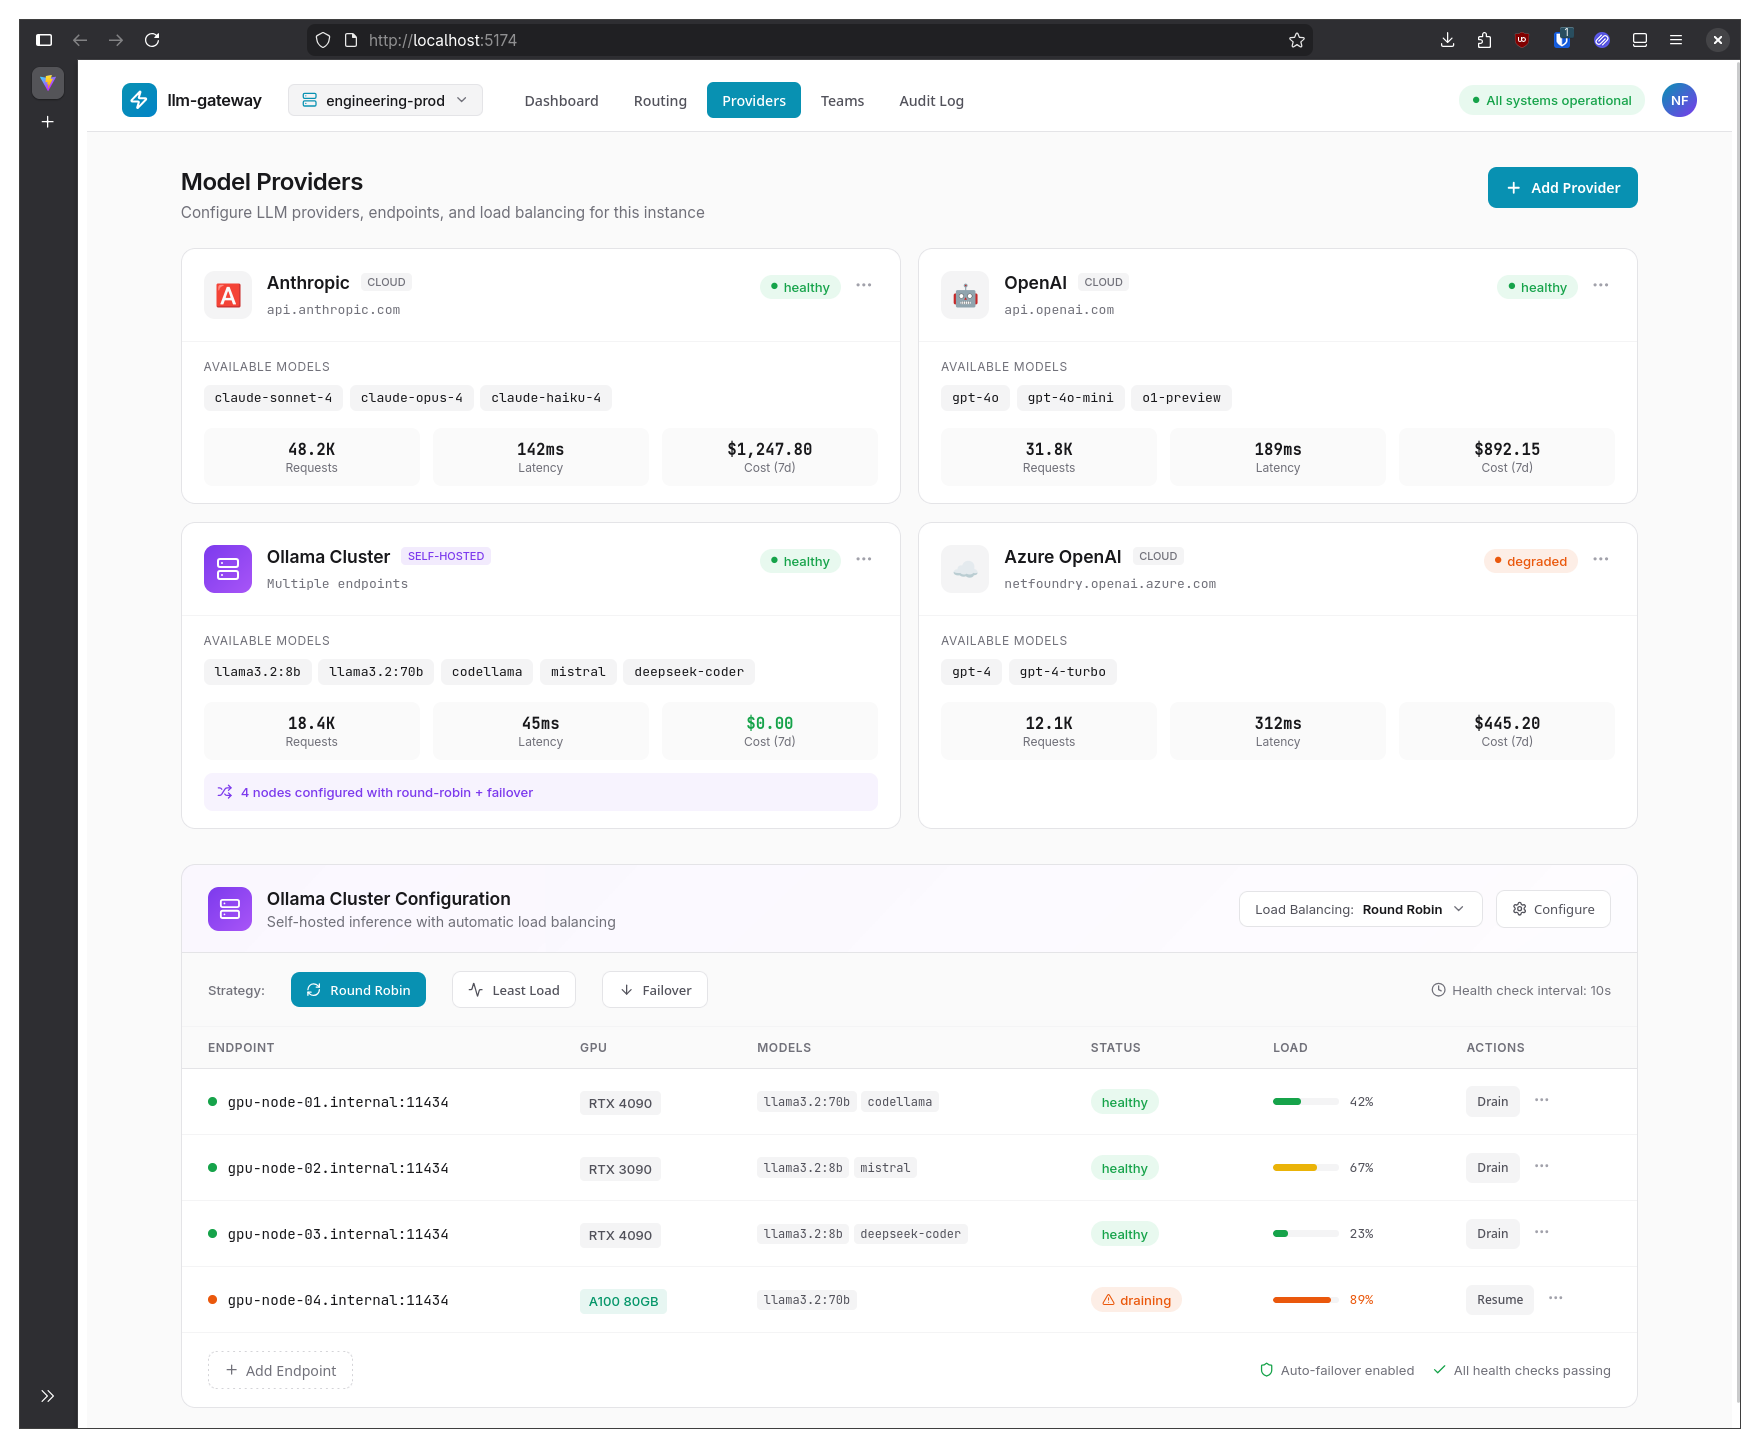
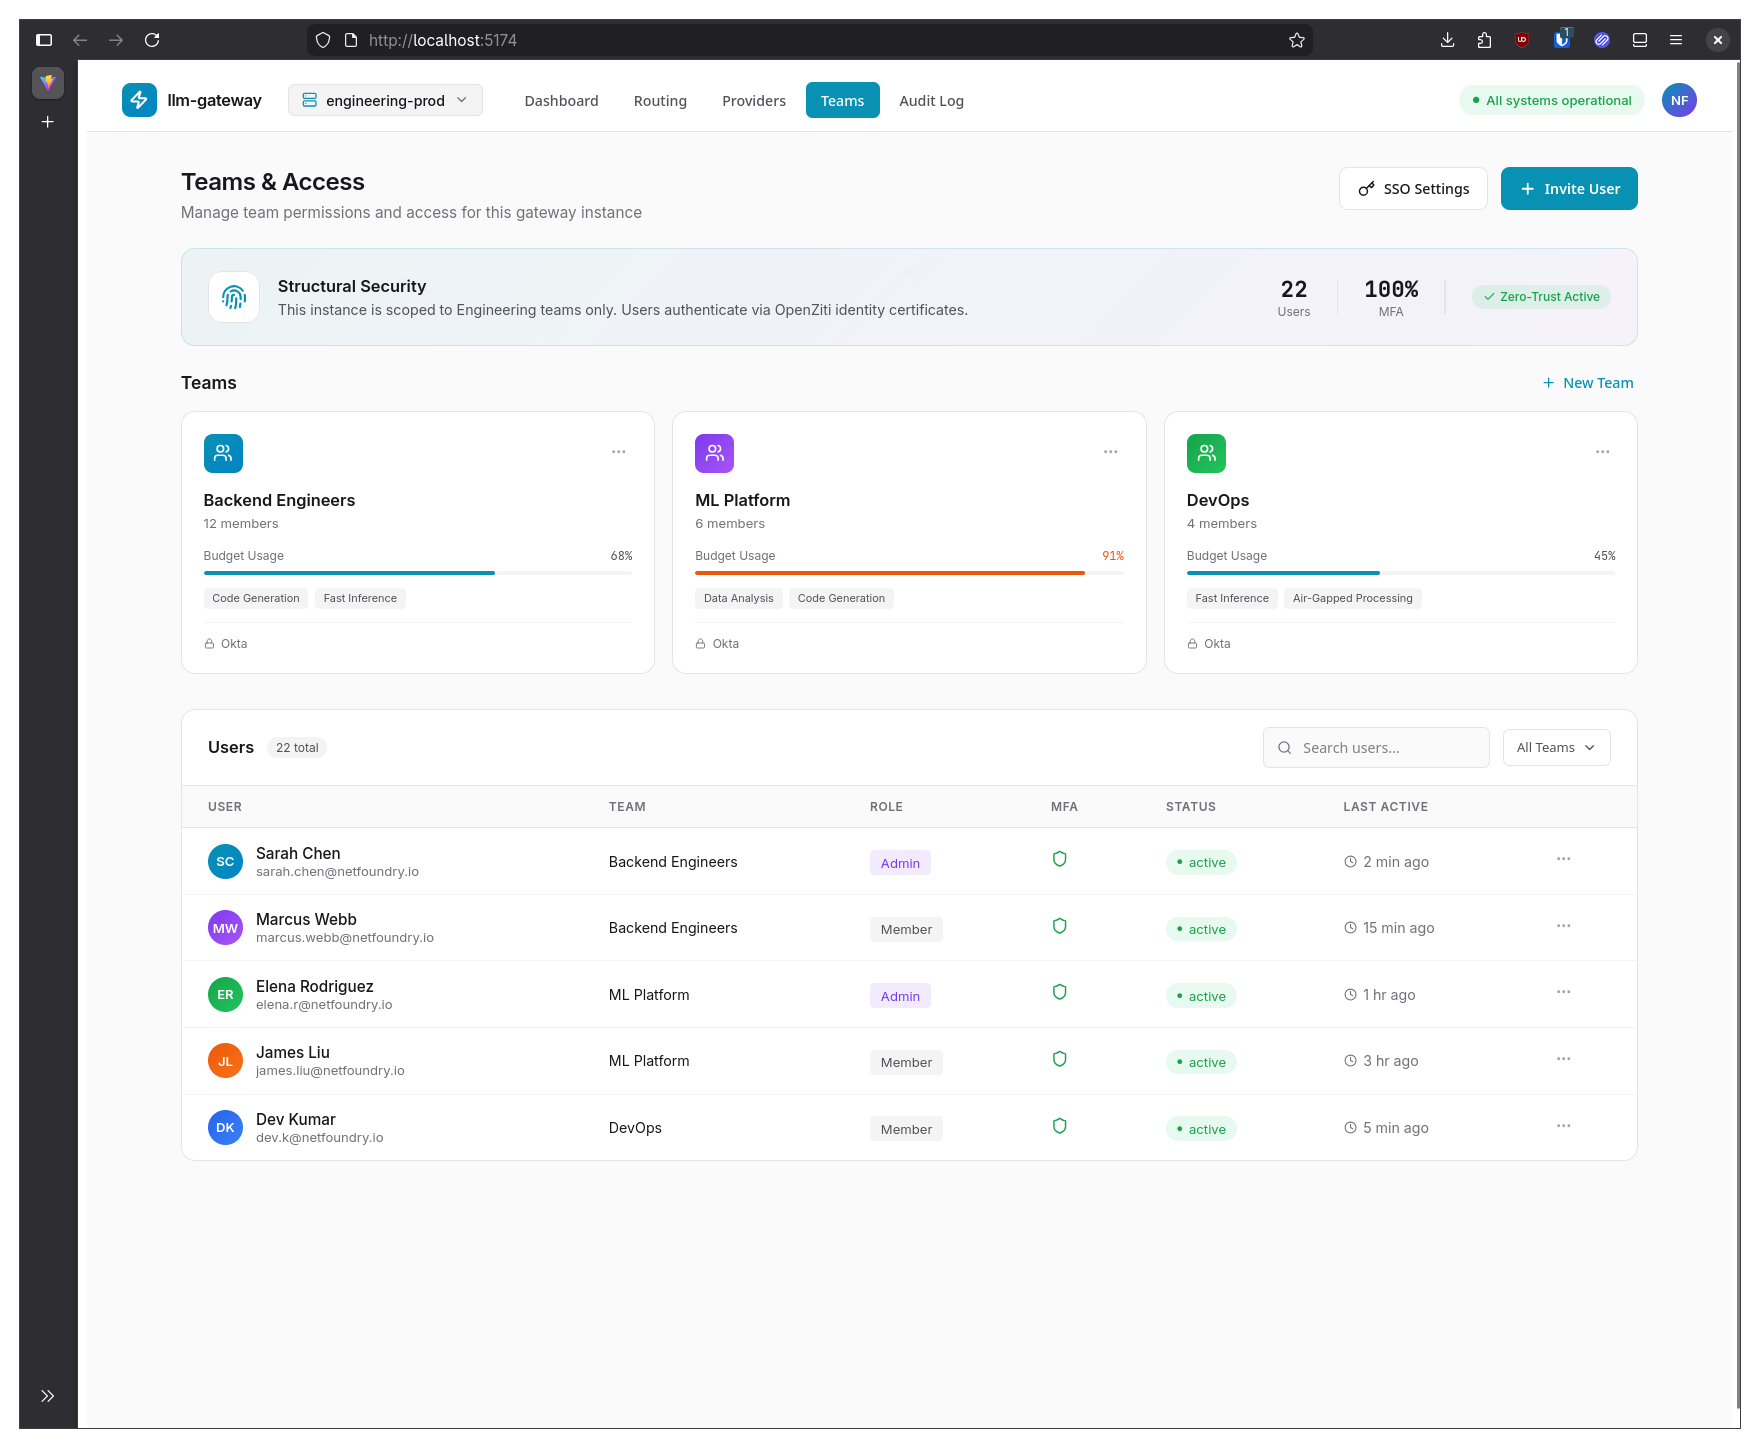
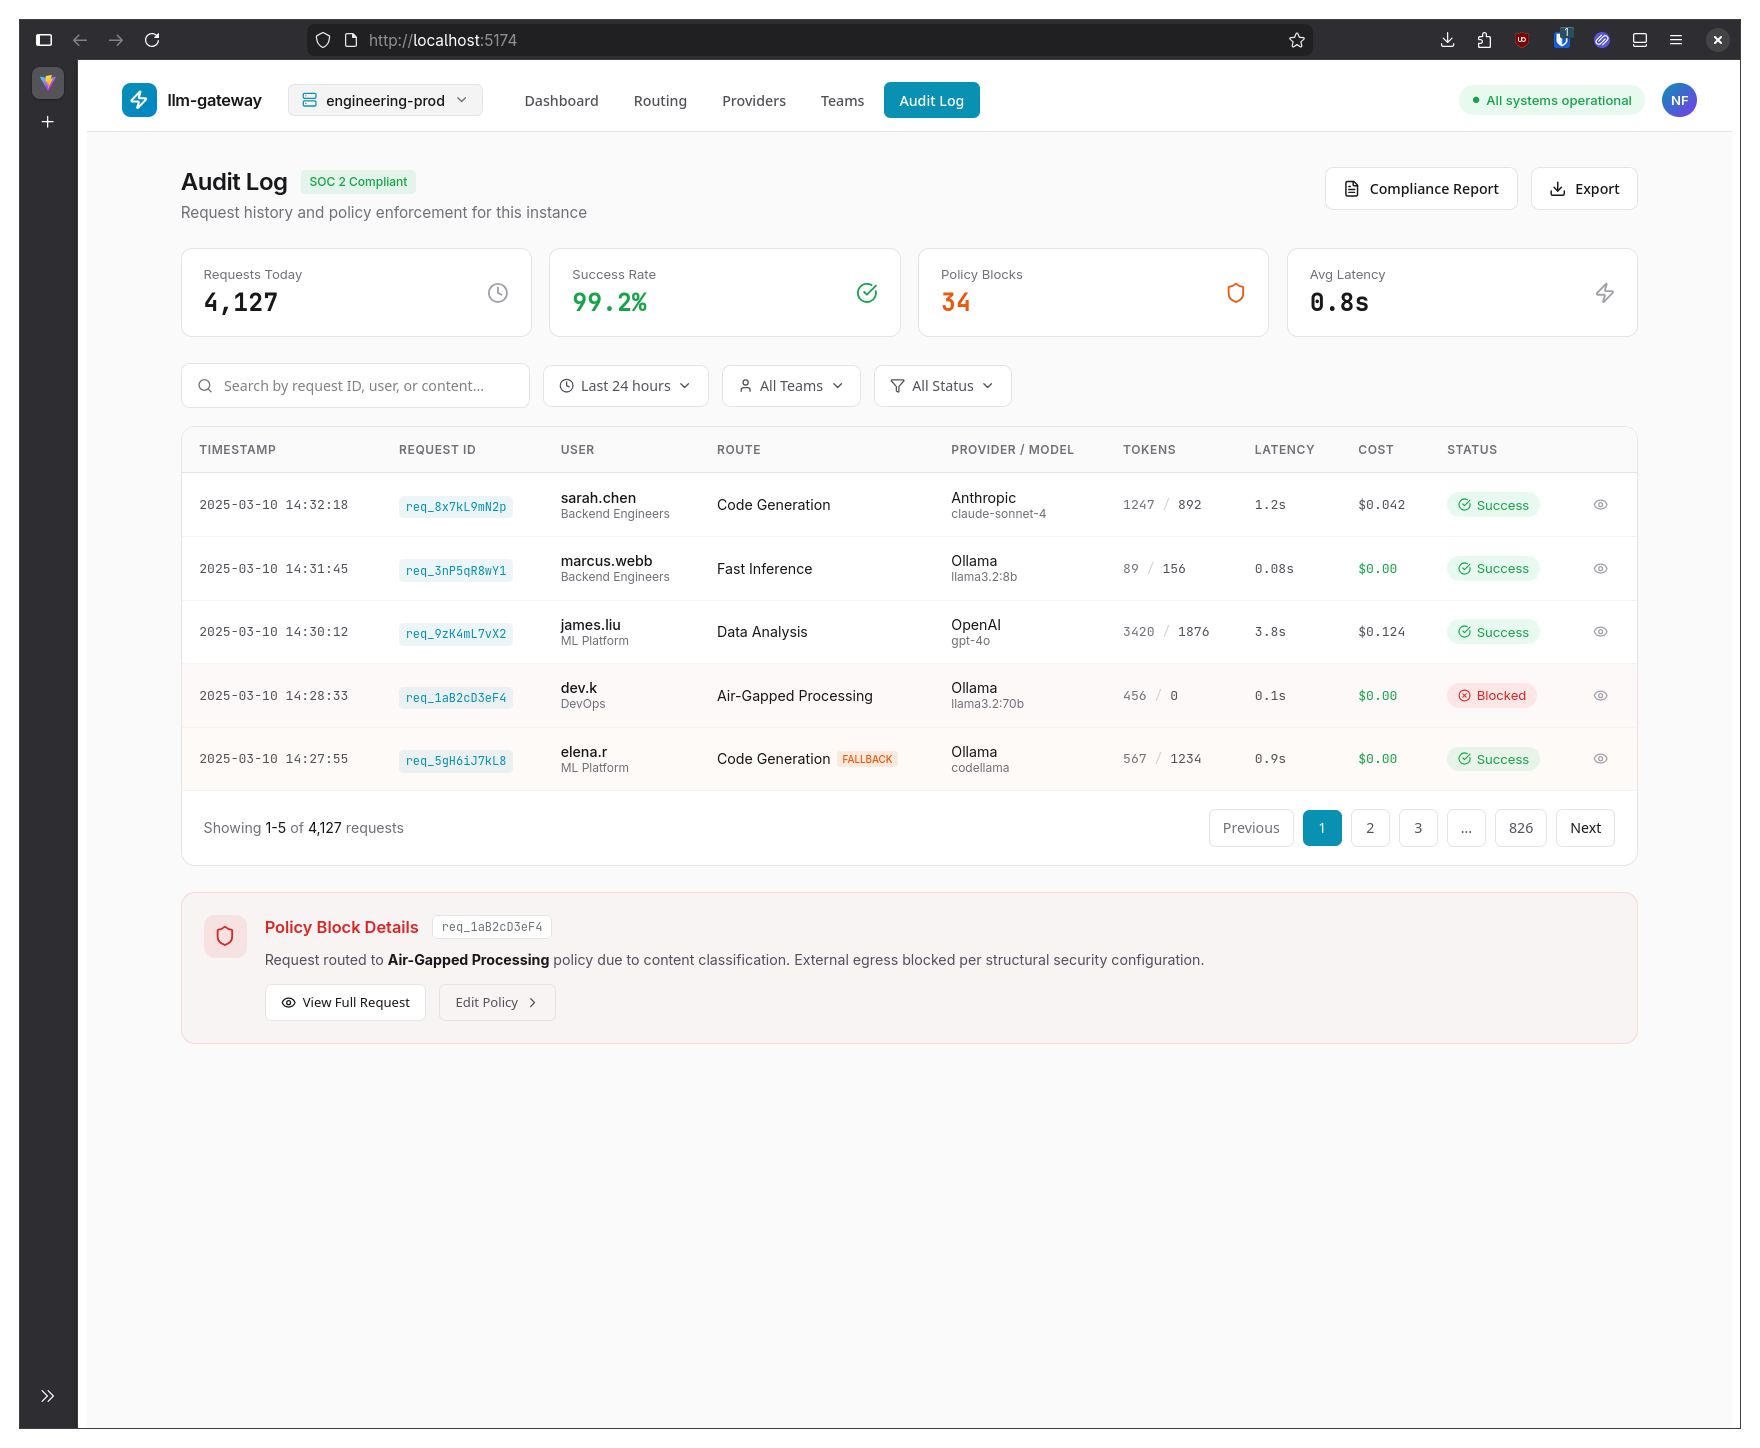
The enclave and gateways are part of a broader AI solution. See all six, including kernel-level agent sandboxing and shipping governed agent fleets in one command.
Get the AI Solution OverviewGovern Access, Spend, and Risk — From One Place
Governance is visibility plus control: seeing what your AI does, and deciding what it’s allowed to do. The AI Enclave gives you both under one identity model, plus the cost and token data finance and security need to keep AI spend accountable.
Cost and token governance
- Budget, cap, and attribute cost and tokens by agent, team, and project
- Finance and security see the same numbers in one place
- Policy stops a runaway agent before it lands on an invoice
Identity-based visibility
- Every request tied to a workload identity, not an IP address
- Auditable record of which agent reached which model, tool, or data source
- One view across every environment and cloud
Instant policy changes
- Grant or revoke access immediately
- Policies defined centrally and updated programmatically
- Control keeps pace with a fast-changing agent ecosystem
“We moved beyond the perimeter with NetFoundry. It delivers a strictly ‘least-privileged’ access model that is incredibly easy to deploy. The management console turns what used to be a tangle of firewall rules into a streamlined, visual command center.”
Viktor Szabó, Deputy CTO, Ominimo
See Governance, Risk Reduction, and Cost Control in Action
Govern it. Secure it. See it. Now You Can Scale it
Every Dollar and Token, Accounted For
- Every dollar and token traces to an owning agent, team, or project
- Finance and security stop reconciling separate numbers
- AI budgets hold without buying another tool
Nothing to Scan, Nothing to Breach
- Nothing sits on the public internet for attackers to scan or reach
- Models, tools, and data stay off every exposed surface
- Exposure-based attacks have no target to aim at
Every Agent Seen, Every Connection Governed
- Teams have no reason to route around security
- Every agent, model, and tool stays visible and governed
- The ungoverned workaround loses its only advantage
Roll Out New AI Tools Without Opening A Single Port
- Workloads connect across clouds, data centers, and the edge
- Outbound-only connections keep every environment free of inbound holes
- New workloads join without firewall changes or network reconfiguration
A Smaller Data Problem, by Design
- Least-privilege access bounds the data any agent can ever touch
- Data governance covers a known set of paths, not every agent everywhere
- Each new model or cloud inherits the same controls instead of restarting the work
Aligned With NIST, CISA, and the International Community
NetFoundry’s identity-first architecture aligns with the AI governance guidance security leaders already answer to, from NIST and CISA to the ISO.
| Framework | What it requires | How NetFoundry aligns |
|---|---|---|
| NIST AI RMF (Govern, Map, Measure) |
Accountable ownership and AI-specific risk management, with repeatable, evidence-based evaluation. | Every agent and connection carries a named, revocable identity and an explicit policy, and per-connection logs give durable, queryable evidence of what an agent actually reached. |
| NIST SP 800-207 & 800-207A (Zero Trust Architecture) |
No implicit trust from network location; per-session, resource-based access decisions; application- and service-level identity across hybrid and multi-cloud. | Identity-first reachability evaluates policy at the moment of connection and enforces one identity model the same way in any cloud, data center, or SaaS tenant. |
| CISA Zero Trust Maturity Model | Optimal maturity across the Identity, Networks, and Applications & Workloads pillars, plus Visibility & Analytics. | Unique workload identity, deny-by-default segmentation to the individual service, least privilege per call, and connection-level logging. |
| CISA, NSA & Five Eyes Agentic AI Guidance (2026) |
Each agent should have its own secure, verifiable identity; least privilege per task; temporary credentials for sensitive actions. | Nearly verbatim the properties this architecture enforces: identity before connectivity, least privilege at the service level, and continuous verification. |
| ISO/IEC 42001 | Demonstrable control over AI components and services sourced from third parties. | An enforced, logged access architecture is direct evidence of that control, not a policy that only describes it. |
Building AI Agents Right Now? Govern Them From Day One.
Join the AI Accelerator Program and stand up a governed enclave for your AI workloads with hands-on help from our team.
“NetFoundry provides the secure network foundation Rhapsody needs to support private, policy-based access across distributed healthcare environments, including applications, APIs, workloads, and emerging AI-enabled workflows. That security layer complements our integration platform by helping customers modernize while protecting mission-critical data exchange.”
Kevin Day, CTO, Rhapsody
Frequently Asked Questions About Zero Trust AI Enclaves
What is a Zero Trust AI Enclave?
NetFoundry’s Zero Trust AI Enclave is a private, policy-governed network fabric that gives every AI agent, LLM, and MCP server its own cryptographic identity and authorizes each connection before a routable path exists. The enclave stays invisible from the internet, requires no open inbound ports or shared API keys, and logs every AI interaction by identity.
How does NetFoundry secure AI agents, LLMs, and MCP servers?
NetFoundry secures AI agents, LLMs, and MCP servers by binding a certificate-based identity to each workload and evaluating policy before it creates any connection. Because every component dials out and nothing listens on an inbound port, models, tools, and data sources stay hidden from internet discovery, scanning, and exploitation.
Does deploying a Zero Trust AI Enclave require firewall changes or open ports?
No. NetFoundry’s Zero Trust AI Enclave uses only outbound, mutually authenticated connections and needs no inbound ports, no firewall changes, no VPN setup, or network reconfiguration. New agents, tools, and models join without opening the network or exposing an endpoint.
How does NetFoundry control AI costs and token spend?
NetFoundry attributes cost and token consumption to the identity of each AI agent, team, and project, and enforces budgets and caps through policy. Finance and security teams see the same numbers in one console, and policy stops a runaway agent before it appears on an invoice.
What is an MCP gateway, and how does NetFoundry’s MCP Gateway work?
NetFoundry’s MCP Gateway authenticates AI agents to Model Context Protocol (MCP) servers with workload identities instead of shared secrets. Each agent discovers and invokes only the tools its policy explicitly permits, which eliminates secret-based access and keeps MCP servers off the public internet.
Can NetFoundry route AI requests between public and private LLMs?
Yes. NetFoundry’s LLM Gateway manages external and internal models from one place with usage policies, load balancing, and failover, and its semantic routing directs each query to a public or a private self-hosted model automatically to optimize for cost and data privacy.
How does a Zero Trust AI Enclave differ from a VPN or firewall approach?
NetFoundry’s Zero Trust AI Enclave authorizes each connection by cryptographic workload identity rather than by IP address, and it verifies identity and policy before any routable path exists. Traditional networks make resources reachable first and authenticate second, which leaves open ports and shared credentials for attackers to find.
How does NetFoundry prevent shadow AI?
NetFoundry prevents shadow AI by making governed AI deployment as fast as the unofficial workarounds that create it. Because connecting a new agent, model, or tool requires no firewall tickets or exposed endpoints, teams gain no speed advantage from unauthorized connections, and every interaction stays visible and policy-controlled.
What is AI access governance?
AI access governance is the practice of controlling which AI agents, LLMs, and MCP servers can reach which models, tools, and data, and at what cost, based on the identity of each workload rather than its network location. NetFoundry delivers AI access governance with a Zero Trust AI Enclave that gives every AI component a cryptographic identity and authorizes each connection by policy before any routable path exists.
How do I see and audit what my AI agents are accessing?
NetFoundry ties every AI connection to the cryptographic identity of the workload that opened it, so you can see which agent, LLM, or MCP server reached which model, tool, or data source, and when. The enclave logs each authorized and denied attempt by identity, which builds a durable, queryable record you can hand to auditors. Because the same identity governs access and records it, your visibility and your enforcement come from one source.
How does NetFoundry align with NIST and CISA guidance for AI?
NetFoundry’s identity-first architecture maps to the AI governance guidance security leaders answer to, including the NIST AI Risk Management Framework, NIST SP 800-207 and 800-207A for Zero Trust, the CISA Zero Trust Maturity Model, the CISA, NSA, and Five Eyes agentic AI guidance, and ISO/IEC 42001. Every AI connection carries a named, revocable identity and an explicit policy, and each authorized or denied attempt is logged as evidence.