
At A Glance
- Recent attacks on refrigeration and other OT systems across Europe have cost operators an estimated tens of millions of dollars, and the root cause is almost always the same: remote access left exposed to the internet.
- A NetFoundry overlay puts every protected device behind a strong, certificate-based identity, so only authorized identities can reach it. That cuts the attacker population from billions of internet hosts down to a handful of known ones.
- The approach is brownfield and inexpensive, with no changes to the control equipment itself, against per-site losses that ran near $10,000 in the recent wave.
Over the past several months, refrigeration systems across Europe have come under sustained attack, and the losses already run into the tens of millions of dollars. I’ve watched this story play out before in water systems and other OT and ICS environments, in different regions, for the same reasons every time. The people who keep these systems running aren’t security engineers, the budgets are thin, and remote access is a hard requirement because vendors, corporate energy teams, and service technicians all need a way in. No one set out to build something insecure. The operational cycles of OT, combined with leadership that isn’t as security-aware as its enterprise IT counterparts, leave doors open that an attacker can walk straight through. I want to lay out a basic design that closes most of those doors, cheaply, for just about any connected system.
Why These Systems Keep Getting Hit
Most of these breaches don’t start with a clever exploit. They start with a device that anyone on the internet can reach: a port-forwarding rule, a vendor VPN, or a management interface left exposed so a technician can log in from the road. Once a device is reachable, its software vulnerabilities and default passwords become somebody else’s opportunity. The OT and ICS workforce is still maturing in cybersecurity, and that gap shows up as shortcuts and weak hygiene far too often. In most of these cases, the exposure is what turns a known weakness into a seven-figure loss.
A Simple Overlay, No Device Changes
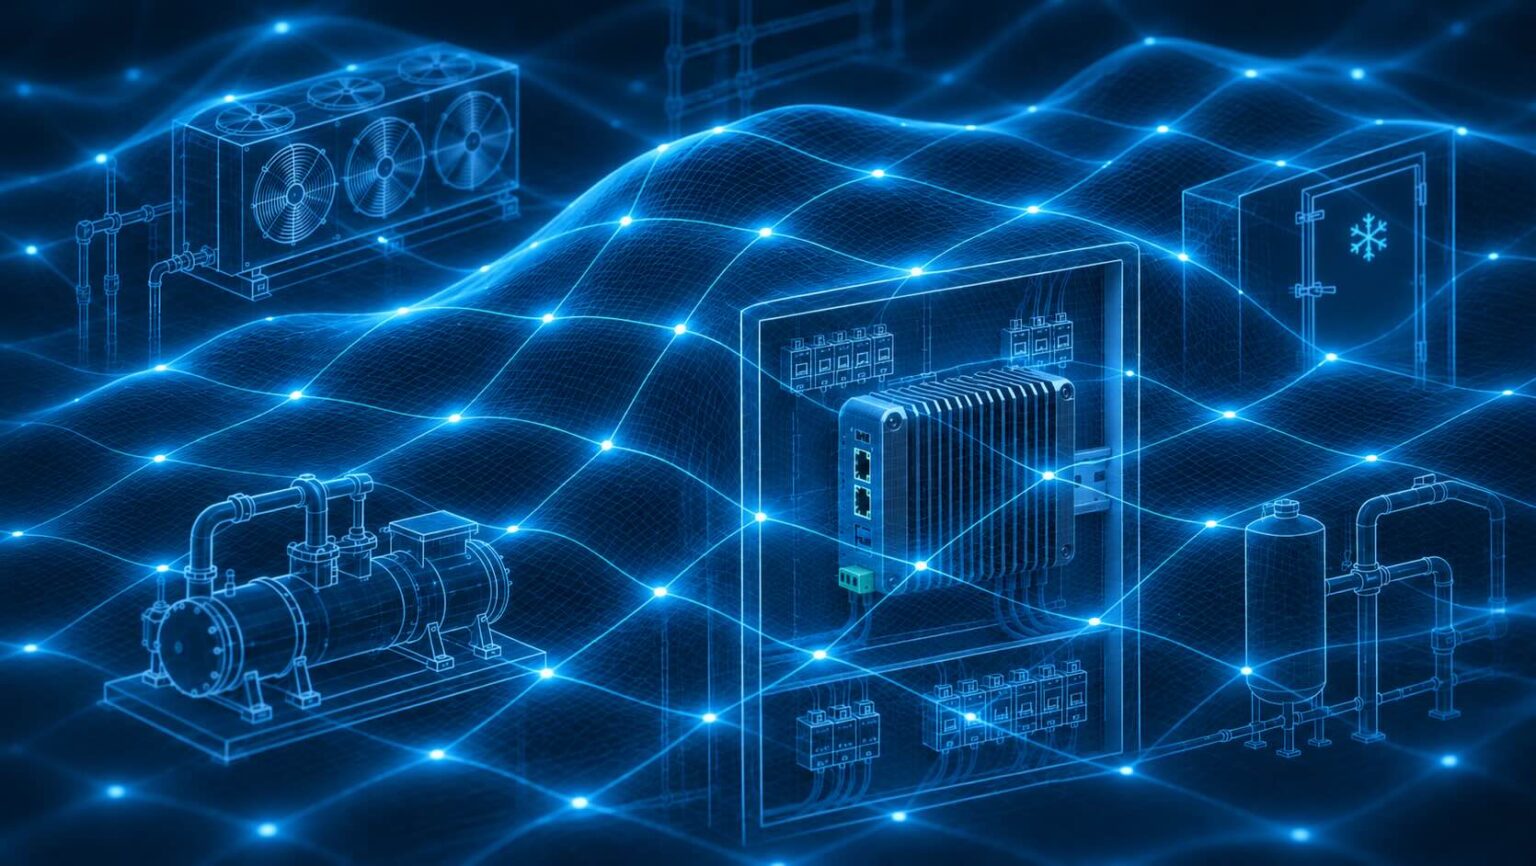
OpenZiti, the open-source technology our team at NetFoundry builds and supports, gives me a way to fix the exposure without touching the equipment. It is a software overlay that runs on top of whatever IP transport a site already uses, which means it adds no new connectivity cost. Three ideas carry the whole model. Identities are strong and backed by X.509 certificates. Services are the specific targets you want to reach, such as a refrigeration controller at a given address and port. Policies decide which identities can host or dial which services.
At each site, I’d drop a small industrial PC in front of the controller to hold the site’s identity and host its service. These fanless units run $400 to $1,000 and tolerate the dust, heat, and humidity that kill ordinary hardware. A node in the head-end’s traffic path intercepts the traffic bound for each site and carries it across the overlay. The control system never knows anything changed.
Shrinking the Attack Surface to a Handful
Here’s what that buys me. The moment a device sits behind a hosted service, it stops answering the open internet and answers only the identities that policy allows. Picture 1,000 connected systems where 999 are site controllers and one is the head-end. Policy lets the head-end dial all 999, and lets none of them dial each other. The attacker population drops from billions of internet hosts to, in practice, a handful of known identities, every one of which has a business reason to be there.
Remote access gets easier at the same time. I can hand a technician an identity and let them connect securely from anywhere, add a cold-chain monitoring platform, or revoke access in seconds, all without touching a firewall or router.
Does the Math Work?
The math works, and it isn’t close. Take the recent refrigeration wave at a conservative $10 million across roughly 1,000 locations. That’s about $10,000 in losses per site. An investment on the order of $1,000 per location would have removed the attack path nearly every one of these incidents relied on. Add the modest cost of a Network Controller and an Edge Router or two, and the return still lands firmly in your favor at even the lowest end of the reported damage.
What This Doesn’t Fix
I want to be honest about the limits. An overlay secures the communication paths. It doesn’t secure the devices themselves. It won’t patch a vulnerable controller or change a default password for you. What it does is shrink who can reach that controller down to people you have authorized. Good operational hygiene, patching, credential rotation, and access audits still matter, and they always will.
Where NetFoundry Fits
Everything I’ve described works with the free, permissively licensed OpenZiti project. NetFoundry, the company behind it, is there when you need enterprise SLAs, 24/7 expert support, and the applications and integrations that make running this at scale simpler and more robust. The design here is the most basic one available, and it’s also the most powerful, because allowing only authenticated, authorized actors to reach your systems cuts the risk by orders of magnitude.
Start Site by Site
If you operate OT or ICS systems that someone, somewhere, can currently reach over the internet, this is the kind of change you can make site by site, on your own schedule, with minimal disruption. See how NetFoundry secures site-to-site and OT connectivity, or talk to us about your environment.
Frequently Asked Questions
Do I have to modify my refrigeration controllers or PLCs?
No. The overlay sits in the network path. The site edge node hosts a service that reaches the device at its existing address and port, so the control system runs unchanged.
Will this disrupt operations during rollout?
Minimally. Each location cuts over independently when its site edge node is installed and powered on, and every other site keeps running throughout the migration.
What does it cost per site?
Roughly $400 to $1,000 for an industrial PC at each location, plus the one-time cost of a Network Controller and one or more Edge Routers for the network as a whole. There is no added connectivity cost, because the overlay rides the IP transport you already use.
Does OpenZiti replace patching and other security basics?
No. It controls who can reach a device, not what is wrong inside it. Keep patching, rotating default credentials, and auditing access.