Step 5: Grant access by IdP group

A service policy grants identities access to services. A Dial policy controls who can use a service, and a Bind policy controls who can host it. Step 4 created the Bind policy. This step creates the Dial policies.
The policies select identities by
role attribute, not
by name. #engineering matches every identity with the engineering attribute. No user identities exist yet.
When alice signs in during step 6, the controller creates her identity with the engineering attribute from her
IdP groups, and this policy already covers her. The administrator writes one policy per group, once, instead of
granting each new user by hand.
The lab's Keycloak realm has two groups, engineering and hr. Each group gets one service:
- ziti CLI
- ZAC
ziti edge create service-policy engineering-dial Dial \
  --identity-roles '#engineering' \
  --service-roles '@eng-wiki'

ziti edge create service-policy hr-dial Dial \
  --identity-roles '#hr' \
  --service-roles '@hr-portal'
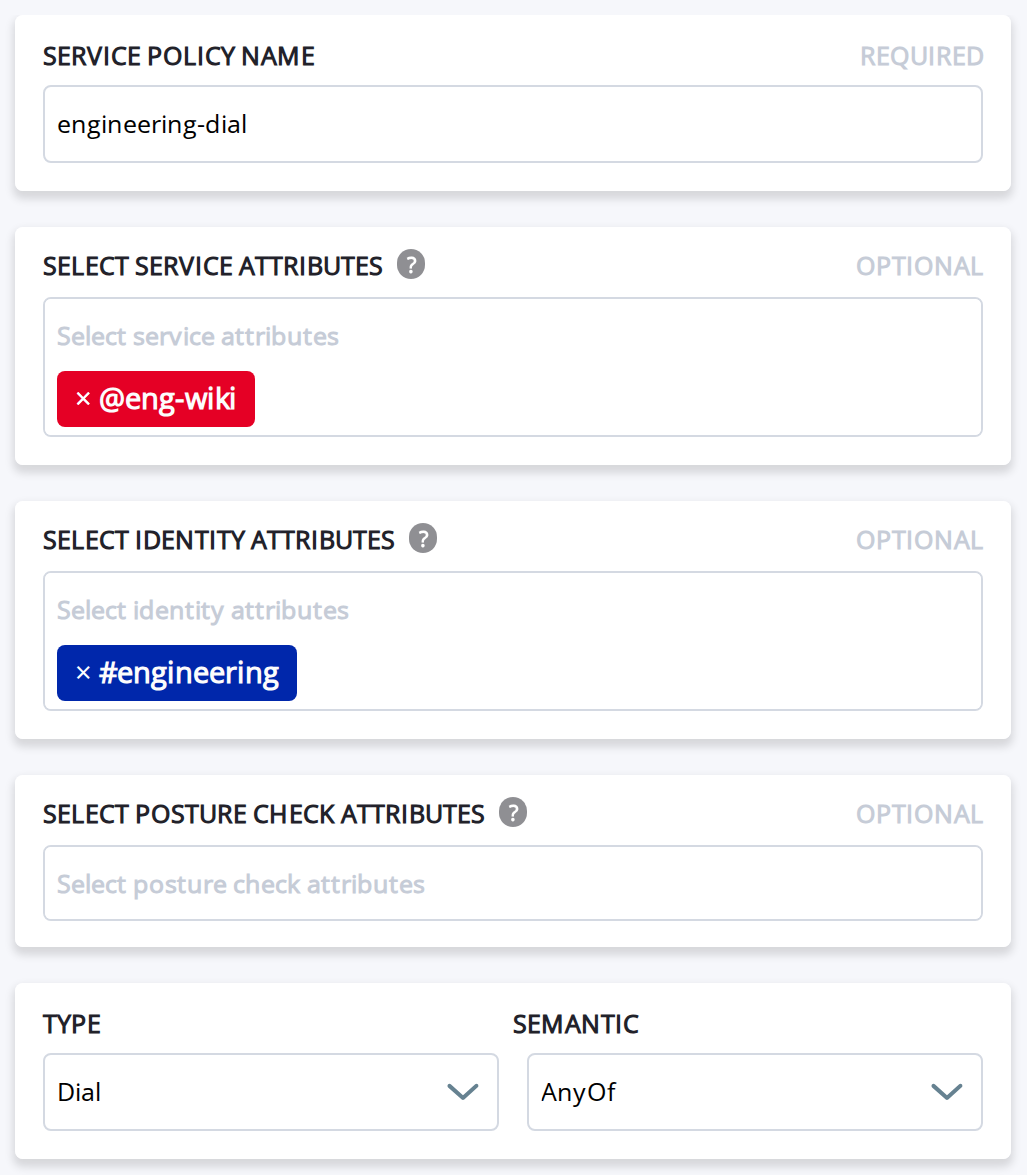
Under Policies > Service Policies, add a Dial policy for each group: engineering-dial for #engineering and
@eng-wiki, and hr-dial for #hr and @hr-portal:
Done when
- A Dial service policy exists for each IdP group that needs access