Step 8 (optional): Map existing identities instead

You don't have to turn on auto enrollment. Without --enroll-to-token and --enroll-to-cert, add by URL still
works, but an administrator creates each identity ahead of time. The identity's external ID has to match the claim
the signer reads, which is email here, and its auth policy has to allow ext-jwt sign-ins.
External JWT signers covers
how that match works.
This step maps carol, who has no IdP group, to an identity the administrator creates.
- ziti CLI
- ZAC
-
Turn off auto enrollment on the signer from step 3:
ziti edge update ext-jwt-signer acme-idp \--enroll-to-token=false \--enroll-to-cert=false -
Create the identity for
carol. Role attributes are set by hand, the same as for any other identity:ziti edge create identity carol \--external-id carol@acme.example \--auth-policy acme-users \--role-attributes engineering
-
Under Authentication > JWT Signers, open
acme-idpand turn off Auto-Enroll to Cert and Auto-Enroll to Token. -
Under Identities, add
carolwith theengineeringattribute, theacme-usersauth policy, and the external IDcarol@acme.example: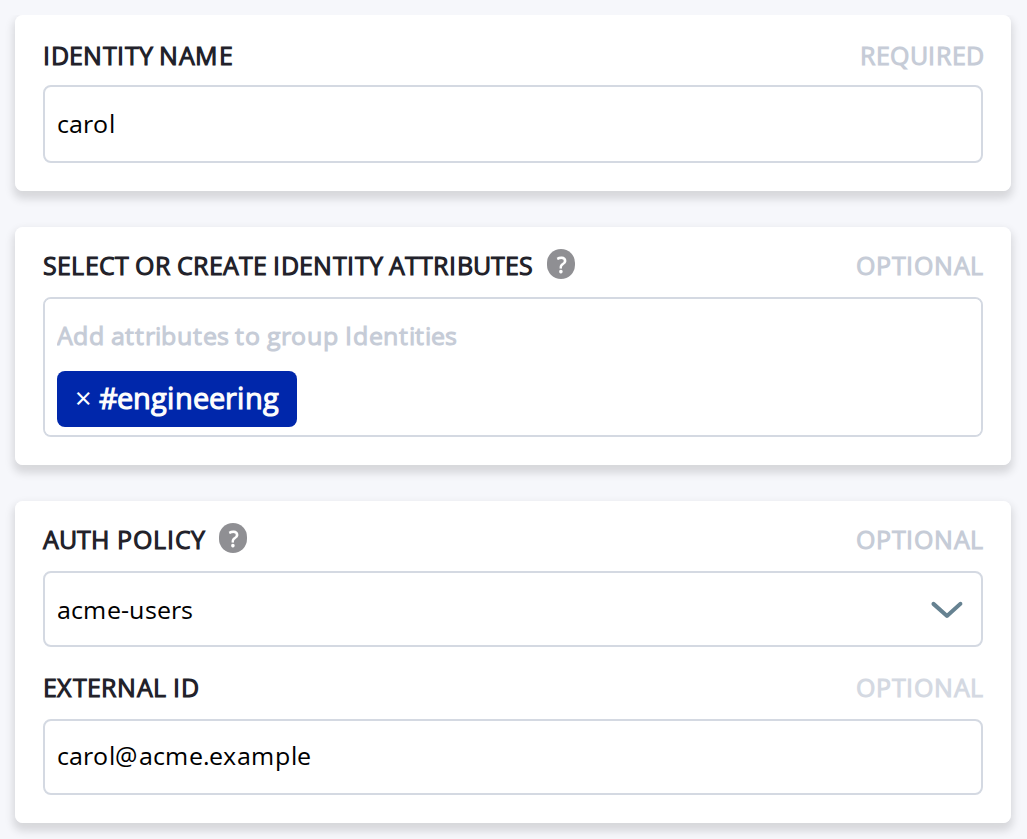
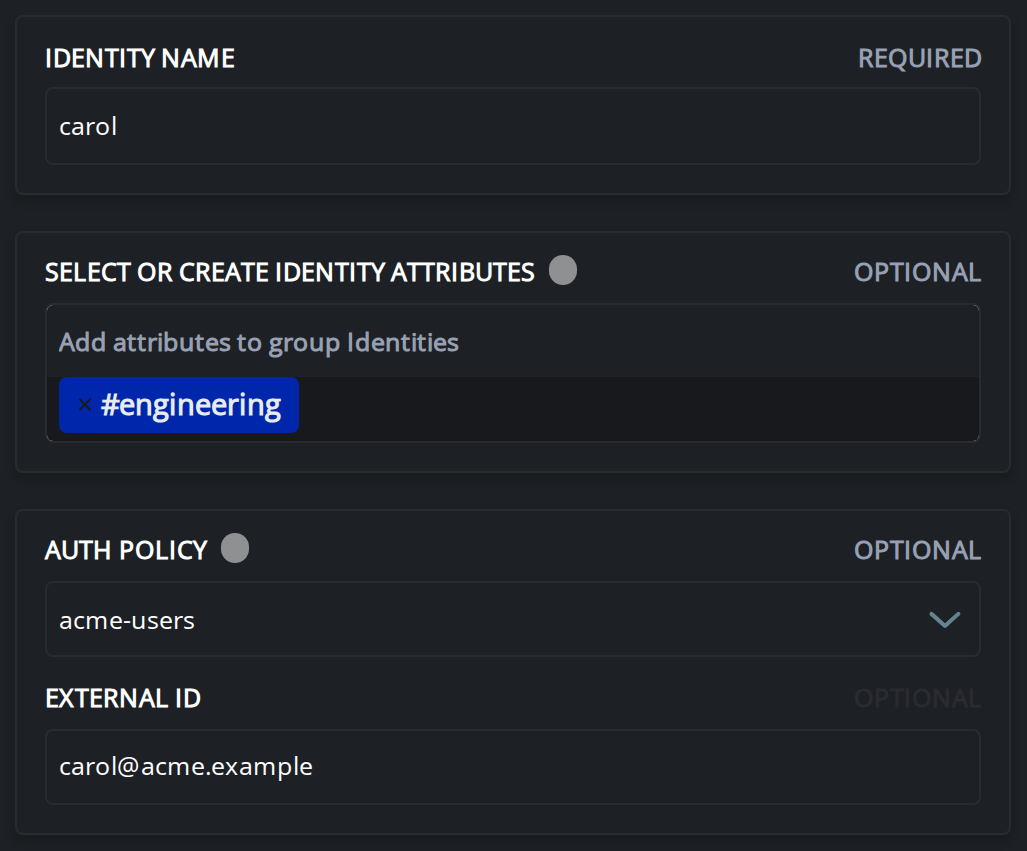
-
As
carol, add the network by URL without--enroll-to-mode, then sign in:sudo ziti-edge-tunnel add \-i carol \-u https://ctrl.example.com:1280sudo ziti-edge-tunnel ext-jwt-login \-i /opt/openziti/etc/identities/carol.json \-p acme-idpWith auto enrollment off,
--enroll-to-mode tokenfails withno compatible ext JWT signer.
In the lab, carol added the network by URL and signed in to Keycloak. The tunneler logged
enroll_mode=none, skipping enrollment and signed in as the carol identity created above. carol stayed one
identity and could reach eng-wiki.
Done when
carolsigns in as the identity you created, and no second identity appearscarolreacheshttp://eng-wiki.acme.ziti